


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 security.nl
NCSC publiceert verbeterd script voor detectie van gehackte Ivanti-servers
Het Nationaal Cyber Security Centrum (NCSC) heeft in samenwerking met Ivanti een verbeterd script gepubliceerd om gehackte Ivanti Endpoint Manager Mobile (EPMM) servers te detecteren en roept Nederlan ...
-
 The Hacker News
Researchers Observe In-the-Wild Exploitation of BeyondTrust CVSS 9.9 Vulnerability
Threat actors have started to exploit a recently disclosed critical security flaw impacting BeyondTrust Remote Support (RS) and Privileged Remote Access (PRA) products, according to watchTowr. "Overni ...
-
 The Cyber Express
8,000+ ChatGPT API Keys Left Publicly Accessible
The rapid integration of artificial intelligence into mainstream software development has introduced a new category of security risk, one that many organizations are still unprepared to manage. Accord ...
-
 CybersecurityNews
Critical Vulnerability in Next-Mdx-Remote Allows Arbitrary Code Execution in React Server-Side Rendering
Vulnerability in Next-Mdx-Remote Security advisory HCSEC-2026-01 revealed a critical vulnerability in the next-mdx-remote library that allows attackers to execute arbitrary code on servers rendering u ...
-
CybersecurityNews
CISA Warns of Notepad++ Code Execution Vulnerability Exploited in Attacks
Notepad++ Code Execution Vulnerability CISA has added CVE-2025-15556 to its Known Exploited Vulnerabilities (KEV) catalog, highlighting active exploitation of a critical code execution flaw in Notepad ...
-
 Daily CyberSecurity
Inside Job: Abandoned Outlook Add-in “AgreeTo” Steals 4,000 Credentials
The phishing page | Image: Koi Security In a disturbing first for enterprise security, researchers at Koi Security have uncovered a malicious Microsoft Outlook add-in actively harvesting credentials i ...
-
Daily CyberSecurity
Triple Threat Patched: Zimbra 10.1.16 Fixes XSS, XXE & LDAP Injection
Zimbra has rolled out a significant security update for its collaboration suite, releasing Zimbra 10.1.16 to address a spectrum of vulnerabilities ranging from front-end script injection to back-end d ...
-
Daily CyberSecurity
Email Under Siege: Storm-2603 Exploits SmarterMail to Deploy Warlock Ransomware
A new report from ReliaQuest has uncovered a dangerous alliance between a China-based threat actor and a known ransomware strain. The group, identified as Storm-2603, has been caught actively exploiti ...
-
Daily CyberSecurity
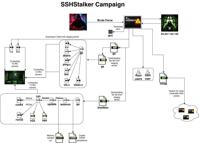
Back to the Future: SSHStalker Botnet Revives 2009 Tactics to Hijack Linux Servers
Image: Flare A previously undocumented Linux botnet has been discovered prowling the internet, using a mix of ancient tactics and modern automation to compromise servers. Dubbed SSHStalker by research ...
-
 reddit.com
Critical RCE Vulnerability in Unstructured.io (CVE-2025–64712) - CVSS 9.8
Let us know your cookie preferences Reddit uses cookies and similar technologies to: Keep the website operational and running properly Prevent fraud and abuse Monitor site usage and performance metric ...