


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 The Hacker News
⚡ Weekly Recap: N-able 0-Days, Windows 0-Days, Chrome 0-Days, Fridge 0-Days, and More Bad Days
A default password opened doors it never should have. A trusted update delivered malware. Even a security feature became a way to break in. Different stories, same problem: the things meant to protect ...
-
 cert.pl
Vulnerabilities in VisualNet visualTicket software
Vulnerabilities in VisualNet visualTicket software CVE ID CVE-2026-113443 Publication date 16 November 2026 Vendor VisualNet Product visualTicket Vulnerable versions All before 20260817 Vulnerability ...
-
cert.pl
Vulnerability in Batflat software
Vulnerability in Batflat software CVE ID CVE-2026-111559 Publication date 16 November 2026 Vendor sruupl Product Batflat Vulnerable versions From 1.2.0 through 1.3.6 Vulnerability type (CWE) Improper ...
-
The Hacker News
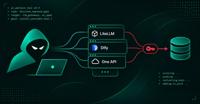
Amazon Uncovers AI Agent Campaign Targeting LiteLLM, Dify, and Other Apps for API Keys
Attackers' AI agents have been hunting for weak spots in internet-exposed AI apps such as LiteLLM, One API, and Dify to steal the AI provider keys stored inside, according to the agents' own records. ...
-
The Hacker News
BO Team Exploits Log4Shell in VMware vCenter, Compromises Russian Firm's Code-Signing Server
An investigation into suspicious activity within a Russian software developer's network has uncovered a months-long compromise of its development infrastructure and a software code-signing server. The ...
-
 TheCyberThrone
PostgreSQL fixes a 22-Year-Old Security Flaw
PostgreSQL released its November 12, 2026 security updates, addressing 52 security vulnerabilities and more than 140 bugs across supported versions.Security Certification GuideThe release deserves at ...
-
The Hacker News
Attackers Exploit UnrealIRCd Flaw That Enables Server-Level Command Injection
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added a high-severity security flaw impacting UnrealIRCd, an open-source Internet Relay Chat (IRC) server, to its Known Explo ...
-
TheCyberThrone
CISA KEV Weekly Roundup – Week 46
12 Exploited Vulnerabilities Across Enterprise Infrastructure, Security Gateways and ApplicationsExploit Prevention ToolsThe CISA KEV Catalog continues to be an important source of exploitation intel ...
-
 Huntress
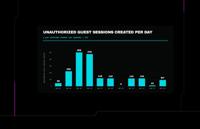
Attackers use Crypto Exchange Names to Disguise Unauthorized Sessions on 100+ ScreenConnect Servers
BackgroundOn November 12, 2026, an MSP asked us about a handful of unfamiliar machines in their self-hosted ScreenConnect console. Named after various crypto exchanges, the machines had no apparent co ...
-
The Hacker News
PostgreSQL Patches 52 Flaws, Including 22-Year-Old Bug Enabling Authenticated RCE
A type confusion flaw in PostgreSQL lets a database user who can create objects run code on the server. Updates released yesterday fix it, along with 51 other security flaws. Full protection from this ...