


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 Daily CyberSecurity
HTTP Down: High-Severity Axios Flaw (CVSS 7.5) Crashes Node.js Servers
A high-severity vulnerability has been discovered in Axios, the immensely popular HTTP client used by millions of developers for Node.js and browser-based applications. The flaw, tracked as CVE-2026-2 ...
-
Daily CyberSecurity
30-Year-Old Bug: High-Severity libpng Flaw (CVSS 8.3) Exposes Millions of Apps
A high-severity vulnerability has been unearthed in libpng, the official and ubiquitous reference library for handling PNG images. The flaw, tracked as CVE-2026-25646, carries a CVSS score of 8.3 and ...
-
 TheCyberThrone
BeyondTrust Remote Support Critical Vulnerability- CVE-2026-1731
February 10, 2026Vulnerability SummaryIdentifier: CVE-2026-1731Severity: Critical (CVSS 4.0 base score ~9.9)Type: Pre-authentication remote code execution (RCE) via OS command injectionAffected Softwa ...
-
Daily CyberSecurity
Triple Threat: Critical Gogs Flaws (CVSS 9.3) Allow RCE & 2FA Bypass
A triple threat of security vulnerabilities has been uncovered in Gogs, the popular self-hosted Git service known for its lightweight footprint. The flaws, tracked as CVE-2025-64111, CVE-2025-64175, a ...
-
Daily CyberSecurity
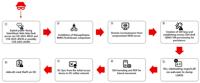
Virtual Invasion: SolarWinds WHD Exploited to Host Hidden QEMU VMs
Image: Microsoft In a striking display of “living off the land” gone wrong, threat actors are turning legitimate administrative tools into stealthy backdoors. The Microsoft Defender Research Team has ...
-
Daily CyberSecurity
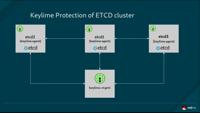
Trust Broken: Critical Keylime Flaw (CVSS 9.4) Disables mTLS Authentication
A critical-severity vulnerability has been discovered in Keylime, the open-source tool used by cloud tenants to verify the integrity of their remote systems. Tracked as CVE-2026-1709, the flaw carries ...
-
Daily CyberSecurity
Silent Killer: Black Basta Bundles “BYOVD” Driver to Blind Antivirus
The notorious Black Basta ransomware group has upgraded its arsenal with a dangerous new capability, embedding defense evasion tools directly inside its ransomware payload. A new report by The Threat ...
-
Daily CyberSecurity
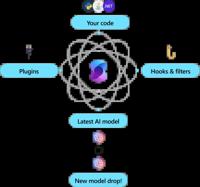
CVE-2026-25592: Critical Semantic Kernel Flaw (CVSS 10.0) Allows File Overwrite
Microsoft has issued a critical security advisory for developers using its Semantic Kernel .NET SDK, warning of a vulnerability that could allow AI agents to overwrite sensitive files on the host syst ...
-
Daily CyberSecurity
CVE-2026-25544: Critical Payload CMS SQLi (CVSS 9.8) Exposes Admin Tokens
A massive security hole has been blown open in Payload, the popular “Next.js native CMS” designed to live directly inside application folders. The vulnerability, tracked as CVE-2026-25544, carries a c ...
-
 The Register
Someone's attacking SolarWinds WHD to steal high‑privilege credentials - but we don't know who or how
Digital intruders exploited buggy SolarWinds Web Help Desk (WHD) instances in December to break into victims' IT environments, move laterally, and steal high-privilege credentials, according to Micros ...