


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 Daily CyberSecurity
Microsoft Patches Four Critical Azure and Power Apps Vulnerabilities, Including CVSS 10 Privilege Escalation
Microsoft has addressed a cluster of critical vulnerabilities affecting several of its core cloud services—including Azure Automation, Azure Storage, Azure DevOps, and Microsoft Power Apps. Although n ...
-
 TheCyberThrone
CVE-2025-46337: Critical SQL Injection Vulnerability in ADOdb PHP Library
CVE-2025-46337 is a high-severity SQL injection vulnerability affecting the ADOdb PHP database abstraction library, which is widely used in web applications for managing database queries across multip ...
-
Daily CyberSecurity
Cisco SD-WAN Vulnerabilities: PoC Exists for XSS and Filter Bypass
Cisco has issued two separate advisories addressing vulnerabilities in its SD-WAN software suite, warning users of potential exploitation risks involving stored cross-site scripting (XSS) and traffic ...
-
Daily CyberSecurity
Radware Cloud WAF Vulnerable to Filter Bypass via Crafted Requests
A newly disclosed vulnerability note by CERT/CC reveals two security flaws (CVE-2024-56523, CVE-2024-56524) in the Radware Cloud Web Application Firewall (WAF) that allow attackers to bypass its filte ...
-
Daily CyberSecurity
Sophisticated IIS Malware Targets South Korean Web Servers
In a targeted and technically advanced cyber operation discovered in February 2025, the AhnLab Security Intelligence Center (ASEC) exposed a sophisticated campaign against South Korean web servers. Th ...
-
Daily CyberSecurity
New Phishing Tactic: Attackers Abuse Blob URIs to Bypass Email Security
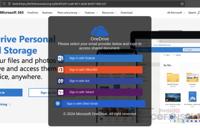
A blob URI page spoofing a OneDrive login | Image: Cofense Cofense Intelligence has detected a new technique used by threat actors to successfully deliver credential phishing pages to users’ inboxes: ...

-
 BleepingComputer
Cisco fixes max severity IOS XE flaw letting attackers hijack devices
Cisco has fixed a maximum severity flaw in IOS XE Software for Wireless LAN Controllers by a hard-coded JSON Web Token (JWT) that allows an unauthenticated remote attacker to take over devices. This t ...
-
 Dark Reading
SonicWall Issues Patch for Exploit Chain in SMA Devices
Source: Sundry Photography via Alamy Stock PhotoSonicWall has fixed three high-severity vulnerabilities affecting its unified secure access gateway devices, one of which has already been exploited in ...
-
 Cyber Security News
New DOGE Big Balls Ransomware Using Open-Source Tools & Custom Scripts to Infect Victim Machines
Cybersecurity researchers have identified a sophisticated new ransomware variant called “DOGE Big Balls,” which appears to be a modified version of the existing Fog ransomware family. The malware, pro ...
-
 The Hacker News
SonicWall Patches 3 Flaws in SMA 100 Devices Allowing Attackers to Run Code as Root
Network Security / Vulnerability SonicWall has released patches to address three security flaws affecting SMA 100 Secure Mobile Access (SMA) appliances that could be fashioned to result in remote code ...