


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 TheCyberThrone
Apache James Denial-of-Service Vulnerabilities
The Apache James Mail Server has recently been identified as vulnerable to two distinct Denial-of-Service (DoS) attacks, tracked as CVE-2024-45626 and CVE-2024-37358 These vulnerabilities pose signifi ...

-
InfoSec Write-ups
Shellshock — A deep dive into CVE-2014–6271
I created a lab to demonstrate this vulnerabilitySource: Photo by BittenTech on YoutubeWhat is Shellshock?Shellshock is a critical vulnerability discovered in 2014 affecting the GNU/Bash shell. It all ...

-
TheCyberThrone
CVE-2025-24503 impacts Symantec PAM
CVE-2025-24503 is a critical security vulnerability affecting Privileged Access Manager (PAM) solutions, specifically those provided by Symantec. This vulnerability, if exploited, can have severe cons ...
-
 The Cloudflare Blog
Resolving a Mutual TLS session resumption vulnerability
2025-02-075 min readOn January 23, 2025, Cloudflare was notified via its Bug Bounty Program of a vulnerability in Cloudflare’s Mutual TLS (mTLS) implementation. The vulnerability affected customers wh ...
-
 BleepingComputer
Hackers exploit Cityworks RCE bug to breach Microsoft IIS servers
Software vendor Trimble is warning that hackers are exploiting a Cityworks deserialization vulnerability to remotely execute commands on IIS servers and deploy Cobalt Strike beacons for initial networ ...
-
 0patch.com
Micropatches Released for Active Directory Certificate Services Elevation of Privilege Vulnerability (CVE-2024-49019)
November 2024 Windows updates brought a fix for CVE-2024-49019, a privilege escalation vulnerability allowing, under specific conditions, a domain user to create a certificate for another domain user, ...

-
 The Register
UK Home Office silent on alleged Apple backdoor order
The UK's Home Office refuses to either confirm or deny reports that it recently ordered Apple to create a backdoor allowing the government to access any user's cloud data. Such a mechanism would enabl ...
-
0patch.com
Micropatches Released for Windows OLE Remote Code Execution (CVE-2025-21298)
January 2025 Windows updates brought a fix for CVE-2025-21298, a memory corruption issue in Windows OLE data processing that can be exploited by a malicious Word document or a malicious email read in ...
-
 The Hacker News
CISA Warns of Active Exploitation in Trimble Cityworks Vulnerability Leading to IIS RCE
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has warned that a security flaw impacting Trimble Cityworks GIS-centric asset management software has come under active exploitation in ...
-
The Hacker News
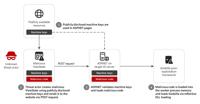
Microsoft Identifies 3,000 Leaked ASP.NET Keys Enabling Code Injection Attacks
Cloud Security / Web Security Microsoft is warning of an insecure practice wherein software developers are incorporating publicly disclosed ASP.NET machine keys from publicly accessible resources, the ...