


CVE-2026-86060
MikroTik RouterOS Improper Neutralization of Argument Delimiters in a Command Vulnerability - [Actively Exploited]
Description
RouterOS contains an argument-handling flaw in the SSH login path involving usernames that begin with a prohibited character, allowing for the trusted RouterOS policy mask to be changed, leading to privilege escalation. Exploitation requires an unauthenticated SSH session to reach the RouterOS login helper.This issue was fixed in versions: 6.49.21 (Long-term), 7.23.4 (Long-term) and 7.24.2 (Stable)
INFO
Published Date :
Sept. 5, 2026, 8:17 p.m.
Last Modified :
Sept. 11, 2026, 12:52 p.m.
Remotely Exploit :
Yes !
Source :
[email protected]
CISA KEV (Known Exploited Vulnerabilities)
For the benefit of the cybersecurity community and network defenders—and to help every organization better manage vulnerabilities and keep pace with threat activity—CISA maintains the authoritative source of vulnerabilities that have been exploited in the wild.
MikroTik RouterOS contains an improper neutralization of argument delimiters in a command vulnerability which allows an attacker to change the trusted RouterOS policy mask, leading to privilege escalation.
Apply mitigations in accordance with vendor instructions, ensuring compliance with CISA’s BOD 26-04 Prioritizing Security Updates Based on Risk (see URL in Notes) guidance and CISA’s “Forensics Triage Requirements” (see URL in Notes). Follow applicable BOD 26-04 guidance for cloud services or discontinue use of the product if mitigations are unavailable. Stakeholders are responsible for evaluating each asset's internet exposure and ensuring adherence to BOD 26-04 patching guidelines.
Unknown
https://mikrotik.com/supportsec/september-2026-vulnerability ; BOD 26-04: https://www.cisa.gov/news-events/directives/bod-26-04-prioritizing-security-updates-based-risk ; Forensics Triage Requirements: https://www.cisa.gov/news-events/directives/bod-26-04-implementation-guidance-prioritizing-security-updates-based-risk ; https://nvd.nist.gov/vuln/detail/CVE-2026-86060
CVSS Scores
| Score | Version | Severity | Vector | Exploitability Score | Impact Score | Source |
|---|---|---|---|---|---|---|
| CVSS | 134c704f-9b21-4f2e-91b3-4a467353bcc0 | |||||
| CVSS 3.1 | CRITICAL | [email protected] | ||||
| CVSS 4.0 | CRITICAL | 4bb8329e-dd38-46c1-aafb-9bf32bcb93c6 | ||||
| CVSS 4.0 | CRITICAL | [email protected] |
Solution
- Update RouterOS to version 6.49.21 or later.
- Update RouterOS to version 7.23.4 or later.
- Update RouterOS to version 7.24.2 or later.
References to Advisories, Solutions, and Tools
Here, you will find a curated list of external links that provide in-depth
information, practical solutions, and valuable tools related to
CVE-2026-86060.
| URL | Resource |
|---|---|
| https://cert.pl/en/posts/2026/09/mikrotik-routeros-cve | Third Party Advisory |
| https://cert.pl/en/posts/2026/09/vulnerabilities-in-mikrotik-routeros-actively-exploited/ | Mitigation Third Party Advisory |
| https://forum.mikrotik.com/t/6-49-21-long-term-is-released/272802 | Release Notes |
| https://forum.mikrotik.com/t/7-23-4-long-term-is-released/272801 | Release Notes |
| https://forum.mikrotik.com/t/7-24-2-stable-is-released/272800 | Release Notes |
| https://mikrotik.com/supportsec/september-2026-vulnerability/ | Vendor Advisory |
| https://npratley.net/reversing-mikrotiks-silent-patch-the-routeros-7-23-4-fix-they-wouldnt-explain/ | Exploit Third Party Advisory |
| https://www.cisa.gov/known-exploited-vulnerabilities-catalog?field_cve=CVE-2026-86060 | US Government Resource |
CWE - Common Weakness Enumeration
While CVE identifies
specific instances of vulnerabilities, CWE categorizes the common flaws or
weaknesses that can lead to vulnerabilities. CVE-2026-86060 is
associated with the following CWEs:
Common Attack Pattern Enumeration and Classification (CAPEC)
Common Attack Pattern Enumeration and Classification
(CAPEC)
stores attack patterns, which are descriptions of the common attributes and
approaches employed by adversaries to exploit the CVE-2026-86060
weaknesses.
We scan GitHub repositories to detect new proof-of-concept exploits. Following list is a collection of public exploits and proof-of-concepts, which have been published on GitHub (sorted by the most recently updated).
Results are limited to the first 15 repositories due to potential performance issues.
The following list is the news that have been mention
CVE-2026-86060 vulnerability anywhere in the article.
-
 The Hacker News
MikroTrick Chain Let Attackers Take Over MikroTik Routers Without a Password or SSH Key
Two MikroTik RouterOS SSH vulnerabilities chained together let attackers take full administrative control of Internet-exposed routers without a password, SSH key, or completed authentication. The chai ... Read more
-
 cert.pl
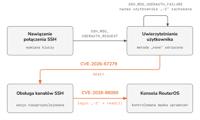
MikroTrick: technical analysis, disclosure process, and the use of LLM agents
Introduction On 3 September 2026, MikroTik released patches almost simultaneously for several maintained RouterOS branches: 7.25beta3, 7.24.2, 7.23.4, and 6.49.21, and recommended installing a patched ... Read more
-
 security.nl
2,6 miljoen MikroTik-routers draaien met publiek toegankelijke services
maandag 14 september 2026, 10:39 door Redactie, 0 reactiesLaatst bijgewerkt: Vandaag, 11:00 Wereldwijd zijn er zo'n 2,6 miljoen MikroTik-routers, waarvan ruim achtduizend in Nederland, die met publiek ... Read more
-
The Hacker News
CISA Adds 5 Actively Exploited Artifactory, ScreenConnect, and RouterOS Flaws to KEV
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added five security flaws impacting JFrog Artifactory, ConnectWise ScreenConnect, and MikroTik RouterOS to its Known Exploited Vuln ... Read more
-
 TheCyberThrone
CISA adds Six Vulnerabilities in Two Days
CISA added six vulnerabilities to the Known Exploited Vulnerabilities (KEV) Catalog across September 10 and 11, 2026.The additions affect MikroTik RouterOS, ConnectWise ScreenConnect, GitLab, and JFro ... Read more
-
 The Cyber Express
Attackers Exploited MikroTik RouterOS Flaws a Day Before Patches Shipped
Attackers began compromising internet-exposed MikroTik routers on Sept. 2, a day before the Latvian vendor released fixes and three days before national authorities published the technical detail defe ... Read more
-
security.nl
MikroTik-routers via kritieke SSH-kwetsbaarheden op afstand overgenomen
Aanvallers maken actief misbruik van kritieke SSH-kwetsbaarheden om routers van fabrikant MikroTik op afstand en zonder authenticatie over te nemen, zo waarschuwen MikroTik en de Poolse overheid. Mikr ... Read more
-
cert.pl
Vulnerabilities in Mikrotik RouterOS software
Vulnerabilities in Mikrotik RouterOS software CVE ID CVE-2026-67276 Publication date 05 September 2026 Vendor Mikrotik Product RouterOS Vulnerable versions From 7.24 below 7.24.2From 7.0.0 below 7.23. ... Read more
-
cert.pl
Critical vulnerabilities in MikroTik RouterOS are being actively exploited. Immediate update recommended
The CERT Polska team has identified and coordinated the disclosure of six vulnerabilities in MikroTik RouterOS. Combining two of them allows an attacker to take full control of the device without auth ... Read more
The following table lists the changes that have been made to the
CVE-2026-86060 vulnerability over time.
Vulnerability history details can be useful for understanding the evolution of a vulnerability, and for identifying the most recent changes that may impact the vulnerability's severity, exploitability, or other characteristics.
-
Initial Analysis by [email protected]
Sep. 11, 2026
Action Type Old Value New Value Added CVSS V3.1 AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H Added CPE Configuration OR *cpe:2.3:o:mikrotik:routeros:*:*:*:*:*:*:*:* versions from (including) 6.0 up to (excluding) 6.49.21 *cpe:2.3:o:mikrotik:routeros:*:*:*:*:*:*:*:* versions from (including) 7.0 up to (excluding) 7.23.4 *cpe:2.3:o:mikrotik:routeros:*:*:*:*:*:*:*:* versions from (including) 7.24 up to (excluding) 7.24.2 Added Reference Type CERT.PL: https://cert.pl/en/posts/2026/09/mikrotik-routeros-cve Types: Third Party Advisory Added Reference Type CERT.PL: https://cert.pl/en/posts/2026/09/vulnerabilities-in-mikrotik-routeros-actively-exploited/ Types: Mitigation, Third Party Advisory Added Reference Type CERT.PL: https://forum.mikrotik.com/t/6-49-21-long-term-is-released/272802 Types: Release Notes Added Reference Type CERT.PL: https://forum.mikrotik.com/t/7-23-4-long-term-is-released/272801 Types: Release Notes Added Reference Type CERT.PL: https://forum.mikrotik.com/t/7-24-2-stable-is-released/272800 Types: Release Notes Added Reference Type CERT.PL: https://mikrotik.com/supportsec/september-2026-vulnerability/ Types: Vendor Advisory Added Reference Type CERT.PL: https://npratley.net/reversing-mikrotiks-silent-patch-the-routeros-7-23-4-fix-they-wouldnt-explain/ Types: Exploit, Third Party Advisory Added Reference Type CISA-ADP: https://www.cisa.gov/known-exploited-vulnerabilities-catalog?field_cve=CVE-2026-86060 Types: US Government Resource -
CVE Modified by 134c704f-9b21-4f2e-91b3-4a467353bcc0
Sep. 11, 2026
Action Type Old Value New Value Changed SSVC {'id': 'CVE-2026-86060', 'role': 'CISA Coordinator', 'options': [{'exploitation': 'active'}, {'automatable': 'yes'}, {'technicalImpact': 'total'}], 'version': '2.0.3', 'timestamp': '2026-09-10T19:48:03.827888Z'} {'id': 'CVE-2026-86060', 'role': 'CISA Coordinator', 'options': [{'exploitation': 'active'}, {'automatable': 'yes'}, {'technicalImpact': 'total'}], 'version': '2.0.3', 'timestamp': '2026-09-08T00:00:00+00:00'} -
CVE CISA KEV Update by 9119a7d8-5eab-497f-8521-727c672e3725
Sep. 10, 2026
Action Type Old Value New Value Added Date Added 2026-09-10 Added Due Date 2026-09-10 Added Required Action 2026-09-10 Added Vulnerability Name 2026-09-10 -
CVE Modified by 134c704f-9b21-4f2e-91b3-4a467353bcc0
Sep. 10, 2026
Action Type Old Value New Value Added Reference https://www.cisa.gov/known-exploited-vulnerabilities-catalog?field_cve=CVE-2026-86060 Changed SSVC {'id': 'CVE-2026-86060', 'role': 'CISA Coordinator', 'options': [{'exploitation': 'none'}, {'automatable': 'yes'}, {'technicalImpact': 'total'}], 'version': '2.0.3', 'timestamp': '2026-09-08T00:00:00+00:00'} {'id': 'CVE-2026-86060', 'role': 'CISA Coordinator', 'options': [{'exploitation': 'active'}, {'automatable': 'yes'}, {'technicalImpact': 'total'}], 'version': '2.0.3', 'timestamp': '2026-09-10T19:48:03.827888Z'} -
CVE Modified by 134c704f-9b21-4f2e-91b3-4a467353bcc0
Sep. 09, 2026
Action Type Old Value New Value Changed SSVC {'id': 'CVE-2026-86060', 'role': 'CISA Coordinator', 'options': [{'exploitation': 'none'}, {'automatable': 'no'}, {'technicalImpact': 'total'}], 'version': '2.0.3', 'timestamp': '2026-09-08T15:43:27.451652Z'} {'id': 'CVE-2026-86060', 'role': 'CISA Coordinator', 'options': [{'exploitation': 'none'}, {'automatable': 'yes'}, {'technicalImpact': 'total'}], 'version': '2.0.3', 'timestamp': '2026-09-08T00:00:00+00:00'} -
CVE Modified by 134c704f-9b21-4f2e-91b3-4a467353bcc0
Sep. 08, 2026
Action Type Old Value New Value Added SSVC {'id': 'CVE-2026-86060', 'role': 'CISA Coordinator', 'options': [{'exploitation': 'none'}, {'automatable': 'no'}, {'technicalImpact': 'total'}], 'version': '2.0.3', 'timestamp': '2026-09-08T15:43:27.451652Z'} -
CVE Modified by [email protected]
Sep. 05, 2026
Action Type Old Value New Value Changed Description RouterOS contains an argument-handling flaw in the SSH login path involving usernames that begin with a prohibited character, allowing for the trusted RouterOS policy mask to be changed, leading to privilege escalation. Exploitation requires an unauthenticated SSH session to reach the RouterOS login helper.This issue was fixed in versions: 6.49.21 (Lont-term), 7.23.4 (Lont-term) and 7.24.2 (Stable) RouterOS contains an argument-handling flaw in the SSH login path involving usernames that begin with a prohibited character, allowing for the trusted RouterOS policy mask to be changed, leading to privilege escalation. Exploitation requires an unauthenticated SSH session to reach the RouterOS login helper.This issue was fixed in versions: 6.49.21 (Long-term), 7.23.4 (Long-term) and 7.24.2 (Stable) -
New CVE Received by [email protected]
Sep. 05, 2026
Action Type Old Value New Value Added Description RouterOS contains an argument-handling flaw in the SSH login path involving usernames that begin with a prohibited character, allowing for the trusted RouterOS policy mask to be changed, leading to privilege escalation. Exploitation requires an unauthenticated SSH session to reach the RouterOS login helper.This issue was fixed in versions: 6.49.21 (Lont-term), 7.23.4 (Lont-term) and 7.24.2 (Stable) Added CVSS V4.0 AV:N/AC:L/AT:P/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N/E:X/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X Added CWE CWE-88 Added Affected New affected value received. <a href="https://github.com/CVEProject/cvelistV5/blob/main/cves/2026/86xxx/CVE-2026-86060.json">CVE-2026-86060</a> Added Reference https://cert.pl/en/posts/2026/09/mikrotik-routeros-cve Added Reference https://cert.pl/en/posts/2026/09/vulnerabilities-in-mikrotik-routeros-actively-exploited/ Added Reference https://forum.mikrotik.com/t/6-49-21-long-term-is-released/272802 Added Reference https://forum.mikrotik.com/t/7-23-4-long-term-is-released/272801 Added Reference https://forum.mikrotik.com/t/7-24-2-stable-is-released/272800 Added Reference https://mikrotik.com/supportsec/september-2026-vulnerability/ Added Reference https://npratley.net/reversing-mikrotiks-silent-patch-the-routeros-7-23-4-fix-they-wouldnt-explain/