


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 BleepingComputer
MongoDB warns admins to patch severe vulnerability immediately
Update 12/26/25: Article updated to correct that the flaw has not been officially classified as an RCE. MongoDB has warned IT admins to immediately patch a high-severity memory-read vulnerability that ...
-
 The Cyber Express
59,000 Servers Breached: Operation PCPcat Targets React and Next.js at Internet Scale
A large-scale cyber espionage operation known as Operation PCPcat has shaken the modern web infrastructure, compromising more than 59,000 servers in just 48 hours. The campaign targets systems built o ...
-
 CybersecurityNews
Critical MongoDB Vulnerability Exposes Sensitive Data via Zlib Compression
A critical security vulnerability, tracked as CVE-2025-14847, that could allow attackers to extract uninitialized heap memory from database servers without authentication. The flaw resides in MongoDB’ ...
-
CybersecurityNews
One Year Of Zero-Click Exploits: What 2025 Taught Us About Modern Malware
The year 2025 represents a pivotal moment in cybersecurity, showcasing a remarkable evolution in zero-click exploitation techniques that significantly challenges our understanding of digital security. ...
-
CybersecurityNews
Operation PCPcat Hacked 59,000+ Next.js/React Servers Within 48 Hours
A massive credential-theft campaign dubbed PCPcat compromised 59,128 Next.js servers in under 48 hours. The operation exploits critical vulnerabilities CVE-2025-29927 and CVE-2025-66478, achieving a 6 ...
-
 TheCyberThrone
From Disclosure to Detonation: CISA KEV Catalog Trends 2025
As 2025 draws to a close, CISA’s Known Exploited Vulnerabilities (KEV) catalog stands as the most critical signal in modern vulnerability management—244 new entries added this year alone, up 28% from ...
-
 Daily CyberSecurity
Racing the Zombie: PoC Released for Linux Kernel POSIX Timer Vulnerability (CVE-2025-38352)
A vulnerability in the Linux kernel’s implementation of POSIX CPU timers has drawn attention following the release of a working proof-of-concept exploit. The flaw, tracked as CVE-2025-38352, is a clas ...
-
Daily CyberSecurity
The Hard-Coded Backdoor: Critical 9.8 Severity NVIDIA Flaws Grant Total Control of AI Systems
NVIDIA has issued an urgent security update for its Isaac Launchable software, patching a trio of critical vulnerabilities that could allow attackers to seize total control of affected systems. The GP ...
-
Daily CyberSecurity
Critical Network Collapse: 9.8 Severity Net-SNMP Buffer Overflow Threatens Global Monitoring Systems
A critical security vulnerability has been found in Net-SNMP, the ubiquitous software suite used globally for network monitoring and management. Tracked as CVE-2025-68615, the flaw carries a near-maxi ...
-
Daily CyberSecurity
“Webrat” Trap: Hackers Lure Junior Security Researchers with Fake GitHub Exploits
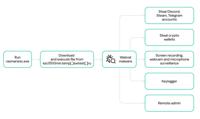
The execution flow and capabilities of rasmanesc.exe | Image: Kaspersky Labs A cunning malware campaign initially designed to trick gamers has evolved into a dangerous trap for aspiring cybersecurity ...