


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 CybersecurityNews
OpenAI GPT-5.2-Codex Supercharges Agentic Coding and Vulnerability Detection
OpenAI has unveiled GPT-5.2-Codex, a cutting-edge model optimized for agentic coding and enhanced cybersecurity tasks. The release highlights breakthroughs in handling complex software engineering and ...
-
 TheCyberThrone
CVE-2025-40602: SonicWall SMA1000 Zero-Day Bug
December 19, 2025SonicWall SMA 1000 and SMA 100 series appliances face a critical local privilege escalation vulnerability, CVE-2025-40602, actively exploited in the wild and often chained with other ...
-
 Daily CyberSecurity
Visualizations Weaponized: New Kibana Flaw Allows XSS Attacks via Vega Charts
Elastic has issued important security updates for Kibana, the popular data visualization dashboard for the Elastic Stack, after discovering a high-severity vulnerability that allows attackers to turn ...
-
Daily CyberSecurity
Log4j’s Security Blind Spot: New TLS Flaw Lets Attackers Intercept Sensitive Logs Despite Encryption
The Apache Software Foundation has released a security update for its widely used Log4j logging library, addressing a moderate-severity vulnerability that could allow attackers to intercept sensitive ...
-
Daily CyberSecurity
WatchGuard Under Siege: Critical CVSS 9.3 Zero-Day Exploited in the Wild to Hijack Corporate Firewalls
A critical zero-day vulnerability has shattered the security perimeter of WatchGuard Firebox appliances, forcing network administrators into a race against time. Tracked as CVE-2025-14733, the flaw ca ...
-
Daily CyberSecurity
Kubernetes Alert: Headlamp Flaw (CVE-2025-14269) Lets Unauthenticated Users Hijack Helm Clusters
A high-severity vulnerability has been discovered in Headlamp, a popular extensible web UI for Kubernetes, potentially allowing unauthenticated attackers to hijack cluster operations. Tracked as CVE-2 ...
-
Daily CyberSecurity
FreeBSD Network Alert: Malicious IPv6 Packets Can Trigger Remote Code Execution via resolvconf (CVE-2025-14558)
A high-severity vulnerability has been uncovered in the FreeBSD networking stack, allowing attackers to execute arbitrary code on vulnerable systems simply by sending a malicious IPv6 router advertise ...
-
Daily CyberSecurity
Roundcube Alert: High-Severity SVG XSS and CSS Sanitizer Flaws Threaten Webmail Privacy
The maintainers of Roundcube Webmail, one of the world’s most widely used open-source email solutions, have issued security updates for their 1.6 and 1.5 LTS branches. The patches address two high-sev ...
-
Daily CyberSecurity
Early-Boot Attack: UEFI Flaw in ASRock, ASUS, & MSI Boards Lets Hackers Bypass OS Security via PCIe
A fundamental breakdown in how modern computers secure themselves during the boot process has been exposed, leaving systems vulnerable to physical attacks that can bypass operating system defenses ent ...
-
Daily CyberSecurity
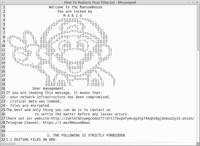
Mario’s Deadly Upgrade: RansomHouse Unveils Dual-Key Encryption to Defeat Backups and Recovery
Ransom Note | Image: Unit 42 Jolly Scorpius, the cybercriminal group behind the notorious RansomHouse operation, has rolled out a major overhaul of its encryption engine, ditching its previously simpl ...