


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 Daily CyberSecurity
Apache SIS Patch Blocks XML Attack That Leaks Server Files
The Apache Software Foundation has issued a security advisory for the Apache Spatial Information System (SIS), a key Java library used for developing geospatial applications. A newly discovered vulner ...
-
Daily CyberSecurity
CVE-2025-66518: High-Severity Flaw in Apache Kyuubi Exposes Local Server Files
Apache Kyuubi, the distributed gateway designed to provide secure, serverless SQL access to massive data lakes, has patched a high-severity vulnerability that could allow unauthorized access to the se ...
-
Daily CyberSecurity
Attacking from Within: How Adobe ColdFusion Admins Can Weaponize Remote Shares
Image: Brian Adobe has issued critical updates for its ColdFusion platform after security researcher Brian Reilly uncovered a clever logic flaw that allows authenticated administrators to turn a stand ...
-
Daily CyberSecurity
MediaTek Kicks Off 2026 with Major Security Overhaul for Mobile Chipsets
MediaTek has kicked off the new year with a critical security bulletin, releasing patches for a slew of high-severity vulnerabilities affecting dozens of its mobile and IoT chipsets. The January 2026 ...
-
Daily CyberSecurity
New TCC Bypass (CVE-2025-43530) Exposes macOS to Unchecked Automation
Apple’s privacy fortress, the Transparency, Consent, and Control (TCC) framework, has been breached once again. Security researcher Mickey Jin (@patch1t) has disclosed a sophisticated new vulnerabilit ...
-
 The Cyber Express
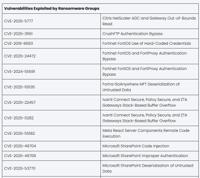
CISA Known Exploited Vulnerabilities Soared 20% in 2025
After stabilizing in 2024, the growth of known exploited vulnerabilities accelerated in 2025. That was one conclusion from Cyble’s analysis of CISA’s Known Exploited Vulnerability (KEV) catalog data f ...
-
 europa.eu
Cyber Brief 26-01 - December 2025
Cyber Brief (December 2025)January 5, 2025 - Version: 1TLP:CLEARExecutive summaryWe analysed 368 open source reports for this Cyber Security Brief[^1].Relating to cyber policy and law enforcement, the ...
-
 The Hacker News
⚡ Weekly Recap: IoT Exploits, Wallet Breaches, Rogue Extensions, AI Abuse & More
Jan 05, 2026Ravie LakshmananHacking News / Cybersecurity The year opened without a reset. The same pressure carried over, and in some places it tightened. Systems people assume are boring or stable ...
-
 CybersecurityNews
Threat Actor Exploited Multiple FortiWeb Appliances to Deploy Sliver C2 for Persistent Access
Recent findings indicate that a sophisticated threat actor is actively exploiting multiple outdated FortiWeb appliances to deploy the Sliver Command and Control (C2) framework. This campaign highlight ...
-
CybersecurityNews
Critical GNU Wget2 Vulnerability Let Remote Attackers to Overwrite Sensitive Files
A critical security vulnerability has been discovered in GNU Wget2, a widely used command-line tool for downloading files from the web. `The flaw, tracked as CVE-2025-69194, allows remote attackers to ...