


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 CybersecurityNews
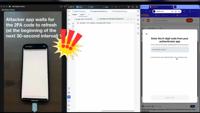
New Pixnapping Attack Steals 2FA Codes From Google Authenticator Within 30 Seconds
Pixnapping, a novel class of side-channel attacks targeting Android devices that can covertly extract sensitive screen data, including two-factor authentication (2FA) codes from Google Authenticator i ...

-
 Medium
CVE Deep Dive : CVE-2025–32463
6 min readSep 23, 2025--Sudo “Chroot to Root” — Critical Library Loading Privilege EscalationPublished : Sept 23, 2025 | by : OptExecutive SummaryRisk Level : Critical (CVSS 9.3) — However : High Risk ...
-
 security.nl
Pixnapping-aanval laat malafide app 2FA-codes van Androidtelefoons stelen
Onderzoekers hebben een nieuwe aanval gedemonstreerd waarmee het mogelijk is voor malafide apps om 2FA-codes en andere gevoelige informatie van besmette Androidtelefoons te stelen. De aanval wordt Pix ...

-
 The Register
Oracle rushes out another emergency E-Business Suite patch as Clop fallout widens
Oracle is rushing out another emergency patch for its embattled E-Business Suite as the fallout from the Clop-linked attacks continues to spread. The newly disclosed flaw, tracked as CVE-2025-61884 an ...
-
 The Cyber Express
Windows 10 Hits End of Life: 200 Million PCs Face Mounting Security Risks
Microsoft has officially ended support for Windows 10, affecting hundreds of millions of users worldwide. This decision comes nearly a decade after the operating system’s initial release and signals t ...
-
 The Hacker News
RMPocalypse: Single 8-Byte Write Shatters AMD’s SEV-SNP Confidential Computing
Oct 14, 2025Ravie LakshmananVulnerability / Hardware Security Chipmaker AMD has released fixes to address a security flaw dubbed RMPocalypse that could be exploited to undermine confidential computi ...
-
The Hacker News
New Pixnapping Android Flaw Lets Rogue Apps Steal 2FA Codes Without Permissions
Oct 14, 2025Ravie LakshmananVulnerability / Mobile Security Android devices from Google and Samsung have been found vulnerable to a side-channel attack that could be exploited to covertly steal two- ...
-
The Cyber Express
Happy DOM Security Flaw (CVE-2025-61927) Enables VM Context Escape and Remote Code Execution
A critical security flaw has been identified in Happy DOM, a widely used JavaScript library primarily employed for server-side rendering and testing frameworks. The vulnerability, cataloged as CVE-202 ...
-
CybersecurityNews
Ivanti Patches 13 Vulnerabilities in Endpoint Manager Allowing Remote Code Execution
Ivanti has disclosed 13 vulnerabilities in its Endpoint Manager (EPM) software, including two high-severity flaws that could enable remote code execution and privilege escalation, urging customers to ...
-
 Daily CyberSecurity
SAP Patches Critical 10.0 Flaw in NetWeaver: Unauthenticated RCE Risk
SAP has released its October 2025 Security Patch Day, addressing 13 new security notes and 3 updates across multiple enterprise products. The update includes a critical vulnerability (CVE-2025-42944) ...