


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 Daily CyberSecurity
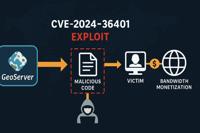
CVE-2024-36401 Exploited in Stealthy Bandwidth-Monetization Campaign
A new report from Palo Alto Networks’ Unit 42 has shed light on an unusual and stealthy monetization campaign that exploits CVE-2024-36401, a critical remote code execution (RCE) vulnerability in GeoS ...
-
Daily CyberSecurity
CVE-2025-9288: Critical Flaw in Popular JavaScript Library Threatens Global Web Security
A critical security vulnerability has been disclosed in sha.js, a widely used JavaScript library that implements the Secure Hash Algorithm (SHA) family. With over 14 million weekly downloads, this lib ...
-
Daily CyberSecurity
DDoS Onslaught: Hacktivists and Botnets Drive Massive Surge in Cyber Attacks
The latest analysis from NETSCOUT highlights a dramatic escalation in botnet-driven distributed denial-of-service (DDoS) attacks during July 2025, with thousands of daily incidents and clear signs of ...
-
 TheCyberThrone
CVE-2018-0171 Years old Cisco Bug exploited
August 21, 2025The CVE-2018-0171 vulnerability is a critical security flaw in Cisco IOS and IOS XE software, specifically affecting the Smart Install feature, which is designed for easy deployment of ...
-
 The Hacker News
Pre-Auth Exploit Chains Found in Commvault Could Enable Remote Code Execution Attacks
Aug 21, 2025Ravie LakshmananVulnerability / Software Security Commvault has released updates to address four security gaps that could be exploited to achieve remote code execution on susceptible ins ...
-
 CybersecurityNews
Threat Actors Gaining Access to Victims’ Machines and Monetizing Access to Their Bandwidth
A stealthy campaign emerged in early March 2025 that capitalized on a critical remote code execution flaw in GeoServer (CVE-2024-36401) to compromise publicly exposed geospatial servers. Attackers exp ...
-
 Help Net Security
Russian threat actors using old Cisco bug to target critical infrastructure orgs
A threat group linked to the Russian Federal Security Service’s (FSB) Center 16 unit has been compromising unpatched and end-of-life Cisco networking devices via an old vulnerability (CVE-2018-0171), ...
-
CybersecurityNews
Mozilla High Severity Vulnerabilities Enables Remote Code Execution
Mozilla has released Firefox 142 to address multiple high-severity security vulnerabilities that could allow attackers to execute arbitrary code remotely on affected systems. The security advisory, pu ...
-
CybersecurityNews
New QUIC-LEAK Vulnerability Let Attackers Exhaust Server Memory and Trigger DoS Attack
A critical pre-handshake vulnerability in the LSQUIC QUIC implementation that allows remote attackers to crash servers through memory exhaustion attacks. The vulnerability, designated CVE-2025-54939 a ...
-
 The Register
Apple rushes out fix for active zero-day in iOS and macOS
Apple has shipped emergency updates to fix an actively exploited zero-day in its ImageIO framework, warning that the flaw has already been abused in targeted attacks. Logged as CVE-2025-43300, the bug ...