


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 seclists.org
SEC Consult SA-20250728-0 :: Stored Cross-Site-Scripting in Optimizely Episerver CMS
Full Disclosure mailing list archives SEC Consult SA-20250728-0 :: Stored Cross-Site-Scripting in Optimizely Episerver CMS From: SEC Consult Vulnerability Lab via Fulldisclosure <fulldisclosure () sec ...
-
seclists.org
SEC Consult SA-20250807-0 :: Race Condition in Shopware Voucher Submission
Full Disclosure mailing list archives SEC Consult SA-20250807-0 :: Race Condition in Shopware Voucher Submission From: SEC Consult Vulnerability Lab via Fulldisclosure <fulldisclosure () seclists org> ...
-
seclists.org
Piciorgros TMO-100: Unauthorized configuration change via TFTP (CVE-2025-29617)
Full Disclosure mailing list archives From: Georg Lukas <lukas () rt-solutions de> Date: Thu, 14 Aug 2025 15:27:20 +0000 <PDF advisory: https://rt-solutions.de/piciorgros/Piciorgros_TMO-100_TFTP_en.pd ...
-
 Daily CyberSecurity
CISA Flags Actively Exploited Trend Micro Apex One Vulnerability (CVE-2025-54948)
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a critical Trend Micro Apex One vulnerability—CVE-2025-54948—to its Known Exploited Vulnerabilities (KEV) Catalog, citing evi ...
-
Daily CyberSecurity
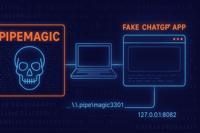
PipeMagic Returns: Kaspersky Uncovers Evolving Backdoor Linked to CVE-2025-29824 Exploits
Kaspersky Labs has released a new report shedding light on the persistent threat posed by PipeMagic, a sophisticated backdoor that has resurfaced in recent attacks against organizations in Saudi Arabi ...
-
 The Cyber Express
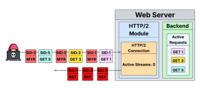
New HTTP/2 DoS Vulnerability Prompts Vendor and Project Fixes
A new HTTP/2 denial of service (DoS) vulnerability that circumvents mitigations put in place after 2023’s “Rapid Reset” vulnerability is largely being addressed by affected vendors and projects, thank ...
-
 Hackread - Latest Cybersecurity, Hacking News, Tech, AI & Crypto
Fake ChatGPT Desktop App Delivering PipeMagic Backdoor, Microsoft
Microsoft warns that a fake ChatGPT desktop app was used to deliver PipeMagic malware, linked to ransomware attacks exploiting a Windows zero-day. Cybersecurity researchers at Microsoft discovered a n ...
-
 BleepingComputer
Over 800 N-able servers left unpatched against critical flaws
Over 800 N-able N-central servers remain unpatched against a pair of critical security vulnerabilities tagged as actively exploited last week. N-central is a popular platform used by many managed serv ...
-
 The Hacker News
Microsoft Windows Vulnerability Exploited to Deploy PipeMagic RansomExx Malware
Aug 18, 2025Ravie LakshmananVulnerability / Cloud Security Cybersecurity researchers have lifted the lid on the threat actors' exploitation of a now-patched security flaw in Microsoft Windows to dep ...
-
 TheCyberThrone
Cisco FMC and FTD Vulnerabilities
August 18, 2025CISCO FMC VulnerabilityCVE-2025-20265 (CVSS 10.0)Description: Remote code execution (RCE) vulnerability in the RADIUS authentication subsystem of FMC. Exploitable remotely and unauthent ...