


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 Daily CyberSecurity
Critical Erlang/OTP Flaw (CVE-2025-32433) Under Active Exploitation, Allowing Unauthenticated RCE on OT Networks
Security researchers at Unit 42 have issued an urgent warning regarding CVE-2025-32433, a CVSS 10.0-rated vulnerability in the Secure Shell (SSH) daemon used by certain versions of the Erlang/OTP fram ...
-
Daily CyberSecurity
Apache bRPC Flaw (CVE-2025-54472) Allows Remote Denial-of-Service Attack
The Apache bRPC project has issued an important security advisory addressing a critical flaw in its Redis protocol parser that could allow attackers to crash affected services remotely. The vulnerabil ...
-
 CybersecurityNews
Erlang/OTP SSH RCE Vulnerability Exploited in the Wild to Attack Across OT Networks
A critical remote code execution vulnerability in Erlang/OTP’s SSH daemon has been actively exploited in the wild, with cybercriminals targeting operational technology networks across multiple industr ...
-
Daily CyberSecurity
GitHub CEO Resigns as Microsoft Integrates the Platform into Its CoreAI Division
In 2018, Microsoft successfully acquired the code hosting platform GitHub for $7.5 billion. At the time, rumors suggested that Google was also preparing a bid, but ultimately Microsoft secured the dea ...
-
Daily CyberSecurity
Record-Breaking Payout: Google Awards $250,000 for a Critical Chrome Flaw (CVE-2025-4609)
A recently disclosed Chromium issue details a critical security vulnerability (CVE-2025-4609) discovered on April 23, 2025, by a security researcher. The flaw, classified as a Chrome browser sandbox e ...

-
 Ars Technica
High-severity WinRAR 0-day exploited for weeks by 2 groups
A high-severity zero-day in the widely used WinRAR file compressor is under active exploitation by two Russian cybercrime groups. The attacks backdoor computers that open malicious archives attached t ...
-
Daily CyberSecurity
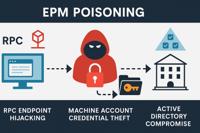
EPM Poisoning (CVE-2025-49760): New Windows RPC Exploit Hijacks Services, Allowing Full Active Directory Compromise, PoC Releases
Security researcher Ron Ben Yizhak from SafeBreach Labs has uncovered a novel attack technique dubbed Endpoint Mapper (EPM) Poisoning, which exploits a core weakness in the Windows Remote Procedure Ca ...
-
CybersecurityNews
UAC‑0099 Tactics, Techniques, Procedures and Attack Methods Unveiled
UAC‑0099, a sophisticated threat actor group that has been active since at least 2022, continues to pose a significant cybersecurity threat through its evolving cyber-espionage campaigns targeting Ukr ...
-
 security.nl
NCSC: Citrix-systemen vitale Nederlandse organisaties gehackt
De Citrix-systemen van meerdere vitale Nederlandse organisaties zijn via een kritieke kwetsbaarheid gehackt, zo laat het Nationaal Cyber Security Centrum (NCSC) vandaag weten. Om welke organisaties he ...
-
 BleepingComputer
Netherlands: Citrix Netscaler flaw CVE-2025-6543 exploited to breach orgs
The Netherlands' National Cyber Security Centre (NCSC) is warning that a critical Citrix NetScaler vulnerability tracked as CVE-2025-6543 was exploited to breach "critical organizations" in the countr ...