


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 Daily CyberSecurity
Linux Kernel Flaw (CVE-2025-38236): Privilege Escalation Risk, PoC Code Available
Security researcher Jann Horn from Google Project Zero disclosed the technical details and proof-of-concept exploit code for a high-severity vulnerability in the Linux kernel — CVE-2025-38236 (CVSS 7. ...
-
Daily CyberSecurity
WinRAR Update: Zero-Day Path Traversal Flaw (CVE-2025-8088) Actively Exploited to Deliver Malware
Security researchers at ESET have uncovered a zero-day path traversal vulnerability in the Windows version of WinRAR that has been actively exploited to execute arbitrary code on victims’ systems. Tra ...
-
 The Register
Trend Micro offers weak workaround for already-exploited critical vuln in management console
Infosec In Brief A critical vulnerability in the on-prem version of Trend Micro's Apex One endpoint security platform is under active exploitation, the company admitted last week, and there's no patch ...
-
 CybersecurityNews
New ‘Win-DoS’ Zero-Click Vulnerabilities Turns Windows Server/Endpoint, Domain Controllers Into DDoS Botnet
LAS VEGAS — At the DEF CON 33 security conference, researchers Yair and Shahak Morag of SafeBreach Labs unveiled a new class of denial-of-service (DoS) attacks, dubbed the “Win-DoS Epidemic.” The duo ...
-
 The Hacker News
New Win-DDoS Flaws Let Attackers Turn Public Domain Controllers into DDoS Botnet via RPC, LDAP
Aug 10, 2025Ravie LakshmananVulnerability / Network Security A novel attack technique could be weaponized to rope thousands of public domain controllers (DCs) around the world to create a malicious ...
-
The Hacker News
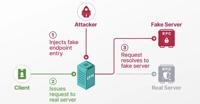
Researchers Detail Windows EPM Poisoning Exploit Chain Leading to Domain Privilege Escalation
Aug 10, 2025Ravie LakshmananVulnerability / Endpoint Security Cybersecurity researchers have presented new findings related to a now-patched security issue in Microsoft's Windows Remote Procedure Ca ...
-
 Hackread - Latest Cybersecurity, Hacking News, Tech, AI & Crypto
AgentFlayer 0-click exploit abuses ChatGPT Connectors to Steal 3rd-party app data
AgentFlayer is a critical vulnerability in ChatGPT Connectors. Learn how this zero-click attack uses indirect prompt injection to secretly steal sensitive data from your connected Google Drive, ShareP ...
-
 Help Net Security
Week in review: SonicWall firewalls targeted in ransomware attacks, Black Hat USA 2025
Here’s an overview of some of last week’s most interesting news, articles, interviews and videos: Black Hat USA 2025 Black Hat USA 2025 took place at the Mandalay Bay Convention Center in Las Vegas. E ...
-
The Hacker News
Researchers Reveal ReVault Attack Targeting Dell ControlVault3 Firmware in 100+ Laptop Models
Aug 09, 2025Ravie LakshmananVulnerability / Hardware Security Cybersecurity researchers have uncovered multiple security flaws in Dell's ControlVault3 firmware and its associated Windows APIs that c ...
-
Hackread - Latest Cybersecurity, Hacking News, Tech, AI & Crypto
WinRAR Zero-Day CVE-2025-8088 Exploited to Spread RomCom Malware
Critical WinRAR flaw CVE-2025-8088 exploited by Russia-linked hackers to spread RomCom malware, update to version 7.13 now to stay protected. Learn how a Russia-linked group is using this vulnerabilit ...