


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 Daily CyberSecurity
MediaTek Chipset Flaws: Out-of-Bounds Write Vulnerabilities Expose Smartphones & IoT Devices
MediaTek, one of the world’s leading chipset manufacturers, has published its latest Product Security Bulletin, revealing several security vulnerabilities affecting a wide range of its chipsets used i ...

-
 InfoSec Write-ups
Living Off the Cloud: Abusing Cloud Services for Red Teaming
Introduction: Blending into the Digital SkylineCyber threats today no longer rely on flashy malware or sketchy infrastructure. Modern adversaries especially Advanced Persistent Threats (APTs) are turn ...
-
Daily CyberSecurity
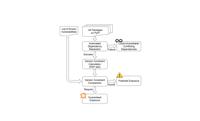
PyPitfall: Python’s Hidden Vulnerabilities Propagate Through 145K+ Packages
The architecture of PyPitfall | Image: The researchers A study from the New Jersey Institute of Technology has exposed a massive web of hidden vulnerabilities lurking deep within Python’s package ecos ...
-
Daily CyberSecurity
Samsung Unveils Exynos 2600: The World’s First 2nm GAA Chip to Power the Galaxy S26
Samsung data breach Bryan Ma, Vice President of Client Devices Research at IDC Asia-Pacific, noted that Samsung is set to debut its flagship Exynos 2600 mobile platform next year, which will be the wo ...
-
Daily CyberSecurity
ShadowSyndicate’s Global Ransomware Empire Blurs Lines Between Cybercrime and Geopolitical Espionage
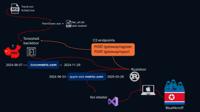
Attack infrastructure of ShadowSyndicate overlaps with Toneshell, Rustdoor and Koi stealer | Image: Intrinsec In a recent investigation, cybersecurity firm Intrinsec has illuminated the sprawling infr ...
-
Daily CyberSecurity
Critical Flaws Found in Partner Software: Default Admin Passwords & XSS Allow RCE on Government Systems
A recent vulnerability note issued by CERT/CC disclosured three critical security flaws in Partner Software’s flagship platforms—Partner Software and Partner Web. These applications are widely used by ...
-
Daily CyberSecurity
Critical RCE Flaw (CVE-2025-54782) in NestJS DevTools Allows Remote Code Execution
A critical vulnerability has been uncovered in the @nestjs/devtools-integration package—a component of the popular NestJS framework for building scalable Node.js applications. This flaw, tracked as CV ...
-
Daily CyberSecurity
The Telecom Threat: Liminal Panda’s Covert Campaign Targets Southwest Asian Critical Infrastructure
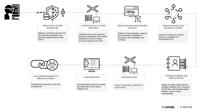
High-level chain of events in the attack investigated by Unit 42 In a revealing report by Palo Alto Networks’ Unit 42, a high-level cyberespionage campaign targeting critical telecommunications infras ...
-
Daily CyberSecurity
Prompt Injection to Code Execution: Cursor Code Editor Hit by Critical MCP Vulnerabilities (CVE-2025-54135 & CVE-2025-54136)
Cursor, an AI-powered code editor that promises to “understand your codebase and help you code faster,” has issued patches for two severe vulnerabilities that could enable remote code execution (RCE) ...
-
Daily CyberSecurity
Storm-2603: Chinese APT Deploys Warlock & LockBit with AK47C2 Framework
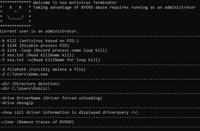
Antivirus Terminator supported arguments when run without parameters | Image: Check Point Check Point Research (CPR) has detailed a previously undocumented Chinese-affiliated threat actor—Storm-2603—l ...