


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 seclists.org
CVE‑2025‑52187 – Stored XSS in School Management System (PHP/MySQL)
Full Disclosure mailing list archives From: Sanjay Singh <sanjay70023 () gmail com> Date: Tue, 22 Jul 2025 18:16:43 +0530 Hello Full Disclosure community, I’m sharing details of a recently assigned CV ...
-
seclists.org
Invision Community <= 5.0.7 (oauth/callback) Reflected Cross-Site Scripting Vulnerability
Full Disclosure mailing list archives From: Egidio Romano <n0b0d13s () gmail com> Date: Wed, 23 Jul 2025 11:58:28 +0200 -------------------------------------------------------------------------------- ...
-
seclists.org
Re: Multiple vulnerabilities in the web management interface of Intelbras routers
=====[Tempest Security Intelligence]========================================== Multiple vulnerabilities in the web management interface of Intelbras routers Author: Gabriel Lima <gabriel lima () tempe ...
-
 CybersecurityNews
Chrome High-Severity Vulnerabilities Allows Memory Manipulation and Arbitrary Code Execution
Google has issued an urgent security update for its Chrome browser, patching several vulnerabilities, including a high-severity vulnerability that could allow attackers to manipulate memory and execut ...
-
 Daily CyberSecurity
Critical Flaw in Wix’s New AI Platform Base44 Allowed Unauthorized Access to Private Enterprise Apps
Image: Wiz Research In a significant finding that highlights the risks associated with emerging AI development platforms, Wiz Research has uncovered a critical vulnerability in Base44, a popular vibe ...
-
Daily CyberSecurity
Critical RCE Flaw (CVE-2025-5394) in “Alone” WordPress Theme Actively Exploited, Allowing Full Site Takeover
A critical-severity vulnerability in the popular Alone – Charity Multipurpose Non-profit WordPress Theme has left thousands of WordPress sites at risk of remote code execution (RCE), according to a re ...
-
Daily CyberSecurity
Gunra Ransomware Expands to Linux: New Variant Unleashes 100-Thread Encryption & Stealthy Tactics
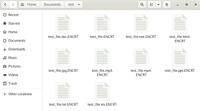
The files encrypted by Gunra Ransomware | Image: Trend Micro Trend Micro has issued a spotlight on the evolving Gunra ransomware, which has extended its reach to Linux-based systems, dramatically broa ...
-
Daily CyberSecurity
TP-Link Archer C50 (EOL) Exposed: Hardcoded DES Key Allows Sensitive Config Decryption (CVE-2025-6982)
The CERT Coordination Center (CERT/CC) has issued a vulnerability note concerning a flaw in the TP-Link Archer C50 router, identified as CVE-2025-6982. The vulnerability arises from the use of hardcod ...
-
Daily CyberSecurity
BeyondTrust Privilege Management for Windows: Two High-Severity Flaws Allow Local Privilege Escalation
BeyondTrust, a global leader in intelligent identity and access security, has issued two advisories addressing two local privilege escalation vulnerabilities in its Privilege Management for Windows pr ...
-
 BleepingComputer
Hackers exploit SAP NetWeaver bug to deploy Linux Auto-Color malware
Hackers were spotted exploiting a critical SAP NetWeaver vulnerability tracked as CVE-2025-31324 to deploy the Auto-Color Linux malware in a cyberattack on a U.S.-based chemicals company. Cybersecurit ...