


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 Cyber Security News
Critical OpenVPN Driver Vulnerability Allows Attackers to Crash Windows Systems
Summary 1. A critical OpenVPN Windows driver flaw (CVE-2025-50054) allowed local attackers to crash systems. 2. The vulnerability enabled denial-of-service attacks but did not expose user data. 3. Ope ...
-
 BleepingComputer
WordPress Motors theme flaw mass-exploited to hijack admin accounts
Hackers are exploiting a critical privilege escalation vulnerability in the WordPress theme "Motors" to hijack administrator accounts and gain complete control of a targeted site. The malicious activi ...
-
 Daily CyberSecurity
Critical Mattermost Flaw (CVE-2025-4981, CVSS 9.9) Allows RCE Via Path Traversal
Open-source collaboration platform Mattermost is exposed to a severe vulnerability that threatens the integrity of its deployments worldwide. Tracked as CVE-2025-4981, this critical flaw (CVSS 9.9) al ...
-
Daily CyberSecurity
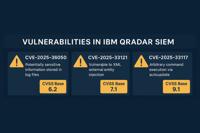
IBM QRadar SIEM Exposed by Trio of Security Flaws, Including Critical Command Execution Bug
IBM has issued a security bulletin addressing three critical vulnerabilities in its QRadar SIEM platform, a widely used solution for security information and event management. The flaws—ranging from l ...
-
 Dark Reading
How to Lock Down the No-Code Supply Chain Attack Surface
Source: Frank Peters via Alamy Stock PhotoCOMMENTARYModern enterprise software development increasingly relies on a vast and complex supply chain of third-party components, integrations, and framework ...

-
Cyber Security News
Insomnia API Client Vulnerability Arbitrary Code Execution via Template Injection
A severe security vulnerability has been discovered in the widely-used Insomnia API Client that allows attackers to execute arbitrary code through malicious template injection. The vulnerability, trac ...

-
InfoSec Write-ups
Everything You Need to Know About CVE-2025–3248: Langflow RCE Vulnerability Explained
CVE-2025–3248: Langflow RCE — When Your AI Pipeline Becomes an Attacker’s PlaygroundIntroductionIn today’s fast-evolving AI ecosystem, frameworks like Langflow are becoming increasingly popular for bu ...
-
 security.nl
WhatsApp: FreeType-lek gebruikt bij aanvallen met Paragon-spyware
Een kwetsbaarheid in FreeType die in maart door Meta werd geopenbaard is gebruikt bij aanvallen met de Graphite-spyware van Paragon Solutions. Dat heeft WhatsApp tegenover SecurityWeek laten weten. Fr ...
-
 cert.pl
TCC Bypass vulnerabilities in two macOS applications
CVE ID CVE-2025-5255 Publication date 20 June 2025 Vendor Core.ai Product Phoenix Code Vulnerable versions All through 4.0.3 Vulnerability type (CWE) Incorrect Default Permissions (CWE-276) Report sou ...
-
 The Cyber Express
CVE-2025-49763: Apache Traffic Server Vulnerability Enables Memory Exhaustion Attacks
A security flaw in Apache Traffic Server (ATS) is targeting cloud service providers worldwide. The vulnerability, identified as CVE-2025-49763, exposes affected systems to denial-of-service (DoS) atta ...