


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 Daily CyberSecurity
UNC1151 Exploits Roundcube Flaw in Spear Phishing Attack
CERT Polska has sounded the alarm after uncovering a spear phishing campaign that targeted Polish organizations using a critical webmail vulnerability. The campaign is linked to the UNC1151 APT group, ...
-
Daily CyberSecurity
Go Fixes Three Security Flaws: Update Your Apps Now!
The Go team has rolled out versions 1.24.4 and 1.23.10, addressing three critical security vulnerabilities affecting core packages such as net/http, os, and crypto/x509. While these are minor point re ...
-
Daily CyberSecurity
FormBook Returns: Exploiting CVE-2017-0199 via Malicious Excel Attachments in New Phishing Campaign
Image: FortiGuard Labs FortiGuard Labs has uncovered a renewed phishing campaign that leverages the eight-year-old CVE-2017-0199 vulnerability to deploy FormBook, a notorious infostealer malware. The ...
-
Daily CyberSecurity
EnigmaCyberSecurity: Brazil-Focused Banking Malware Campaign Uses RATs and Malicious Extensions
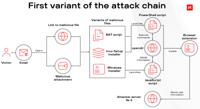
Attack chain using a browser extension | Image: Positive Technologies Positive Technologies has uncovered an ongoing, multi-stage cybercrime campaign—dubbed “EnigmaCyberSecurity”—primarily targeting B ...
-
Daily CyberSecurity
CVE-2025-4318 (CVSS 9.5): AWS Amplify RCE Flaw Exposed with PoC – CI/CD Pipelines at Risk
Image: SecureLayer7 A critical vulnerability in AWS Amplify’s UI generation tool, @aws-amplify/codegen-ui, is putting developers—and their build pipelines—at serious risk. Tracked as CVE-2025-4318, th ...
-
 The Register
US infrastructure could crumble under cyberattack, ex-NSA advisor warns
Infosec in Brief If a cyberattack hit critical infrastructure in the US, it would likely crumble, former deputy national security adviser and NSA cybersecurity director Anne Neuberger said last week. ...
-
 BleepingComputer
New Mirai botnet infect TBK DVR devices via command injection flaw
A new variant of the Mirai malware botnet is exploiting a command injection vulnerability in TBK DVR-4104 and DVR-4216 digital video recording devices to hijack them. The flaw, tracked under CVE-2024- ...
-
 security.nl
Microsoft komt met script voor herstellen inetpub-map op Windowssystemen
Microsoft heeft een script uitgebracht om de inetpub-map op Windowssystemen te herstellen als gebruikers deze map verwijderd hebben. Eerder waarschuwde het techbedrijf al dat gebruikers deze map niet ...
-
 Help Net Security
Week in review: Google fixes exploited Chrome zero-day, Patch Tuesday forecast
Here’s an overview of some of last week’s most interesting news, articles, interviews and videos: June 2025 Patch Tuesday forecast: Second time is the charm? Microsoft has been busy releasing more out ...
-
Daily CyberSecurity
New Mirai Botnet Variant Targets DVR Systems via CVE-2024-3721
Kaspersky researchers have uncovered a fresh wave of attacks exploiting CVE-2024-3721 to deploy a revamped variant of the notorious Mirai botnet — and this time, the target is a vulnerable class of DV ...