


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 seclists.org
83 vulnerabilities in Vasion Print / PrinterLogic
Full Disclosure mailing list archives 83 vulnerabilities in Vasion Print / PrinterLogic From: Pierre Kim <pierre.kim.sec () gmail com> Date: Tue, 8 Apr 2025 13:48:18 -0400 Hello, Please find a text-on ...
-
seclists.org
[CVE-2025-32102, CVE-2025-32103] SSRF and Directory Traversal in CrushFTP 10.7.1 and 11.1.0 (as well as legacy 9.x)
Full Disclosure mailing list archives From: Rafael Pedrero <rafael.pedrero () gmail com> Date: Fri, 4 Apr 2025 08:01:00 +0200 <!-- # Exploit Title: Server-Side Request Forgery (SSRF) in CrushFTP 10.7. ...
-
seclists.org
Re: APPLE-SA-03-11-2025-2 iOS 18.3.2 and iPadOS 18.3.2
Full Disclosure mailing list archives From: Nick Boyce <nick.boyce () gmail com> Date: Sat, 5 Apr 2025 23:42:53 +0100 [Complete Apple product novice here (my devices all run a non-Apple OS), but I'm a ...

-
seclists.org
[KIS-2025-01] UNA CMS <= 14.0.0-RC4 (BxBaseMenuSetAclLevel.php) PHP Object Injection Vulnerability
Full Disclosure mailing list archives From: Egidio Romano <n0b0d13s () gmail com> Date: Mon, 7 Apr 2025 17:29:13 +0200 --------------------------------------------------------------------------------- ...
-
seclists.org
OXAS-ADV-2025-0001: OX App Suite Security Advisory
Full Disclosure mailing list archives OXAS-ADV-2025-0001: OX App Suite Security Advisory From: Martin Heiland via Fulldisclosure <fulldisclosure () seclists org> Date: Mon, 7 Apr 2025 09:11:36 +0200 ( ...
-
 Cyber Security News
Cybersecurity Weekly Recap: Key Updates on Attacks, Vulnerabilities, & Data Breaches
Welcome to this week’s Cybersecurity Newsletter, providing you with the latest updates and essential insights from the rapidly evolving field of cybersecurity. This edition highlights emerging threats ...

-
 TheCyberThrone
CVE-2025-32896 impacts Apache SeaTunnel
CVE-2025-32896 is a critical vulnerability discovered in Apache SeaTunnel, a widely used distributed data integration platform. This flaw allows unauthenticated attackers to exploit insecure REST API ...
-
 Help Net Security
Week in review: Microsoft patches exploited Windows CLFS 0-day, WinRAR MotW bypass flaw fixed
Here’s an overview of some of last week’s most interesting news, articles, interviews and videos: Microsoft fixes actively exploited Windows CLFS zero-day (CVE-2025-29824) April 2025 Patch Tuesday is ...

-
 Daily CyberSecurity
CVE-2025-32896: Apache SeaTunnel Flaw Enables Unauthenticated File Read & RCE
A newly disclosed vulnerability, CVE-2025-32896, in Apache SeaTunnel—a widely used distributed data integration platform—could allow unauthenticated attackers to read arbitrary files and execute deser ...
-
Daily CyberSecurity
SVG Phishing Surge: How Image Files Are Being Weaponized to Steal Credentials
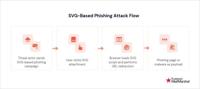
SVG-Based Phishing Attack Flow | Image: Trustwave SpiderLabs In a world where images are meant to inform or entertain, a new breed of phishing attack is using them to deceive and steal. A recent repor ...