


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 The Cyber Express
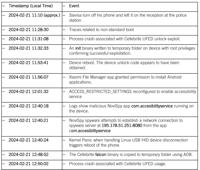
New Android Spyware Detected in Serbian Surveillance Investigation
In February 2024, Serbian journalist Slaviša Milanov was taken to a police station following what seemed like a routine traffic stop. But after his release, the phone that he’d been asked to leave wit ...

-
 cybereason.com
CVE-2024-55956: Zero-Day Vulnerability in Cleo Software Could Lead to Data Theft
Key Takeaways Zero-day vulnerability was discovered in 3 Cleo products, tracked as CVE-2024-55956 Cleo is the developer of various managed file transfer platforms with approximately 4,000 customers, m ...

-
 TheCyberThrone
Detailing Critical Microsoft CVE-2024-49112 Vulnerability
Microsoft has recently disclosed a critical Remote Code Execution (RCE) vulnerability in its Lightweight Directory Access Protocol (LDAP) service, identified as CVE-2024-49112 Released as part of the ...
-
 BleepingComputer
New critical Apache Struts flaw exploited to find vulnerable servers
A recently patched critical Apache Struts 2 vulnerability tracked as CVE-2024-53677 is actively exploited using public proof-of-concept exploits to find vulnerable devices. Apache Struts is an open-so ...
-
 security.nl
'Tienduizenden SonicWall-firewalls online bevatten kritiek lek of zijn end-of-life'
Tienduizenden firewalls van fabrikant SonicWall die vanaf het internet benaderbaar zijn bevatten kritieke kwetsbaarheden of zijn end-of-life. Dat stelt securitybedrijf Bishop Fox op basis van eigen on ...
-
 Hackread - Latest Cybersecurity, Tech, Crypto & Hacking News
Hackers Use Fake PoCs on GitHub to Steal WordPress Credentials, AWS Keys
SUMMARY Fake PoCs on GitHub: Cybercriminals used trojanized proof-of-concept (PoC) code on GitHub to deliver malicious payloads to unsuspecting users, including researchers and security professionals. ...
-
security.nl
FBI waarschuwt voor aanvallen op ip-camera's en digitale videorecorders
Aanvallers maken misbruik van bekende kwetsbaarheden en zwakke wachtwoorden om ip-camera's en digitale videorecorders van onder andere Hikvision, D-Link en Dahua met malware te infecteren, zo waarschu ...
-
 The Hacker News
The Mask APT Resurfaces with Sophisticated Multi-Platform Malware Arsenal
Cyber Espionage / Mobile Security A little-known cyber espionage actor known as The Mask has been linked to a new set of attacks targeting an unnamed organization in Latin America twice in 2019 and 20 ...
-
The Hacker News
CISA and FBI Raise Alerts on Exploited Flaws and Expanding HiatusRAT Campaign
Network Security / IoT Security The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday added two security flaws to its Known Exploited Vulnerabilities (KEV) catalog, citing evidenc ...

-
 seclists.org
[KIS-2024-07] GFI Kerio Control <= 9.4.5 Multiple HTTP Response Splitting Vulnerabilities
Full Disclosure mailing list archives From: Egidio Romano <n0b0d13s () gmail com> Date: Mon, 16 Dec 2024 19:27:17 +0100 --------------------------------------------------------------------------- GFI ...