


CVE-2023-50224
TP-Link TL-WR841N Authentication Bypass by Spoofing Vulnerability - [Actively Exploited]
Description
TP-Link TL-WR841N dropbearpwd Improper Authentication Information Disclosure Vulnerability. This vulnerability allows network-adjacent attackers to disclose sensitive information on affected installations of TP-Link TL-WR841N routers. Authentication is not required to exploit this vulnerability. The specific flaw exists within the httpd service, which listens on TCP port 80 by default. The issue results from improper authentication. An attacker can leverage this vulnerability to disclose stored credentials, leading to further compromise. Was ZDI-CAN-19899.
INFO
Published Date :
May 3, 2024, 3:16 a.m.
Last Modified :
Sept. 3, 2026, 5:28 p.m.
Remotely Exploit :
No
Source :
[email protected]
CISA KEV (Known Exploited Vulnerabilities)
For the benefit of the cybersecurity community and network defenders—and to help every organization better manage vulnerabilities and keep pace with threat activity—CISA maintains the authoritative source of vulnerabilities that have been exploited in the wild.
TP-Link TL-WR841N contains an authentication bypass by spoofing vulnerability within the httpd service, which listens on TCP port 80 by default, leading to the disclose of stored credentials. The impacted products could be end-of-life (EoL) and/or end-of-service (EoS). Users should discontinue product utilization.
Apply mitigations per vendor instructions, follow applicable BOD 22-01 guidance for cloud services, or discontinue use of the product if mitigations are unavailable.
Unknown
https://www.tp-link.com/us/support/faq/4308/ ; https://nvd.nist.gov/vuln/detail/CVE-2023-50224
Affected Products
The following products are affected by CVE-2023-50224
vulnerability.
Even if cvefeed.io is aware of the exact versions of the
products
that
are
affected, the information is not represented in the table below.
CVSS Scores
| Score | Version | Severity | Vector | Exploitability Score | Impact Score | Source |
|---|---|---|---|---|---|---|
| CVSS | 134c704f-9b21-4f2e-91b3-4a467353bcc0 | |||||
| CVSS 3.0 | MEDIUM | [email protected] | ||||
| CVSS 3.1 | MEDIUM | [email protected] |
Public PoC/Exploit Available at Github
CVE-2023-50224 has a 1 public
PoC/Exploit available at Github.
Go to the Public Exploits tab to see the list.
References to Advisories, Solutions, and Tools
Here, you will find a curated list of external links that provide in-depth
information, practical solutions, and valuable tools related to
CVE-2023-50224.
| URL | Resource |
|---|---|
| https://www.tp-link.com/en/support/download/tl-wr841n/v12/#Firmware | Product |
| https://www.tp-link.com/us/support/faq/5058/ | Vendor Advisory |
| https://www.zerodayinitiative.com/advisories/ZDI-23-1808/ | Third Party Advisory |
| https://www.tp-link.com/en/support/download/tl-wr841n/v12/#Firmware | Product |
| https://www.zerodayinitiative.com/advisories/ZDI-23-1808/ | Third Party Advisory |
| https://www.cisa.gov/known-exploited-vulnerabilities-catalog?field_cve=CVE-2023-50224 | US Government Resource |
CWE - Common Weakness Enumeration
While CVE identifies
specific instances of vulnerabilities, CWE categorizes the common flaws or
weaknesses that can lead to vulnerabilities. CVE-2023-50224 is
associated with the following CWEs:
Common Attack Pattern Enumeration and Classification (CAPEC)
Common Attack Pattern Enumeration and Classification
(CAPEC)
stores attack patterns, which are descriptions of the common attributes and
approaches employed by adversaries to exploit the CVE-2023-50224
weaknesses.
We scan GitHub repositories to detect new proof-of-concept exploits. Following list is a collection of public exploits and proof-of-concepts, which have been published on GitHub (sorted by the most recently updated).

AI-powered home network security scanner and threat dashboard
CSS HTML JavaScript Python
Results are limited to the first 15 repositories due to potential performance issues.
The following list is the news that have been mention
CVE-2023-50224 vulnerability anywhere in the article.
-
 The Cyber Express
FBI Takes Down APT28 Network Behind Global DNS Hijacking Attacks
The Russian-linked threat group APT28 has continued to leverage vulnerable network devices to carry out large-scale DNS hijacking campaigns, enabling adversary-in-the-middle attacks. Recent developmen ... Read more
-
 Daily CyberSecurity
APT28 Hijacks Home Routers to Steal Corporate Credentials
In a major technical disclosure, the UK National Cyber Security Centre (NCSC) has detailed a sophisticated campaign by the Russian threat actor APT28 (also known as Fancy Bear or Forest Blizzard). The ... Read more
-
 The Hacker News
Russian State-Linked APT28 Exploits SOHO Routers in Global DNS Hijacking Campaign
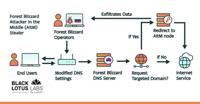
The Russia-linked threat actor known as APT28 (aka Forest Blizzard) has been linked to a new campaign that has compromised insecure MikroTik and TP-Link routers and modified their settings to turn the ... Read more
-
 Help Net Security
Russian hackers hijack internet traffic using vulnerable routers
The Russian state cyber group APT28 has been compromising routers to hijack web traffic and spy on victims, the UK’s The National Cyber Security Centre (NCSC) has warned. Attackers are exploiting vuln ... Read more
-
 The Register
CISA sounds alarm over TP-Link wireless routers under attack
Infosec in brief The US Cybersecurity and Infrastructure Security Agency (CISA) has said two flaws in routers made by Chinese networking biz TP-Link are under active attack and need to be fixed – but ... Read more
-
 TheCyberThrone
CISA Adds Sitecore, Linux Kernel, and TP-Link Flaws to KEV Catalog
September 7, 2025The Cybersecurity and Infrastructure Security Agency (CISA) has expanded its Known Exploited Vulnerabilities (KEV) catalog, flagging new security threats that are actively being explo ... Read more
-
 BleepingComputer
New TP-Link zero-day surfaces as CISA warns other flaws are exploited
TP-Link has confirmed the existence of an unpatched zero-day vulnerability impacting multiple router models, as CISA warns that other router flaws have been exploited in attacks. The zero-day vulnerab ... Read more
-
The Hacker News
CISA Flags TP-Link Router Flaws CVE-2023-50224 and CVE-2025-9377 as Actively Exploited
Sep 04, 2025Ravie LakshmananVulnerability / Network Security The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added two security flaws impacting TP-Link wireless routers ... Read more
-
 security.nl
TP-Link waarschuwt voor botnet dat routers besmet en M365-accounts kaapt
TP-Link waarschuwt voor een botnet dat verschillende kwetsbaarheden gebruikt om kwetsbare routers te infecteren, die vervolgens worden gebruikt voor het aanvallen van Microsoft 365-accounts. De beveil ... Read more
The following table lists the changes that have been made to the
CVE-2023-50224 vulnerability over time.
Vulnerability history details can be useful for understanding the evolution of a vulnerability, and for identifying the most recent changes that may impact the vulnerability's severity, exploitability, or other characteristics.
-
Modified Analysis by [email protected]
Sep. 03, 2026
Action Type Old Value New Value Added CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-wr841n_firmware:*:*:*:*:*:*:*:* versions from (including) 11_150616 up to (excluding) 11_211209 OR cpe:2.3:h:tp-link:tl-wr841n:11:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-wr841n_firmware:*:*:*:*:*:*:*:* versions from (including) 12_160624 up to (excluding) 12_230317 OR cpe:2.3:h:tp-link:tl-wr841n:12:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:mr6400_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:mr6400:1.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:mr6400:2.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-wdr3600_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:tl-wdr3600:2.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-wdr4300_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:tl-wdr4300:1:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:wdr3500_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:wdr3500:2.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-wr710n_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:tl-wr710n:1.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:tl-wr710n:2.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-wr740n_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:tl-wr740n:4.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:tl-wr740n:5.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:tl-wr740n:6.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:tl-wr740n:7.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-wr741nd_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:tl-wr741nd:5:*:*:*:*:*:*:* cpe:2.3:h:tp-link:tl-wr741nd:2.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:tl-wr741nd:4.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:tl-wr741nd:6.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-wr743nd_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:tl-wr743nd:2.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:wr749n_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:wr749n:6.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:wr749n:7.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:mr3420_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:mr3420:2.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:mr3420:3.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:mr3420:4.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:wr1043nd_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:wr1043nd:2.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:wr1043nd:3.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:wr1043nd:4.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:wr1045nd_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:wr1045nd:2.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:wr802n_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:wr802n:1.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:wr802n:2.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:wr802n:3.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-wr810n_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:tl-wr810n:1.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:tl-wr810n:2.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-wr840n_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:tl-wr840n:2.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:tl-wr840n:3.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:wr841hp_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:wr841hp:2.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:wr841hp:3.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-wr841nd_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:tl-wr841nd:11.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:wr842n_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:wr842n:2.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:wr842n:3.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:wr842n:4.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:wr842nd_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:wr842nd:2.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:wr842nd:3.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:wr842nd:4.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-wr843n_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:tl-wr843n:2.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:tl-wr843n:3.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:wr845n_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:wr845n:1.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:wr845n:2.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:wr945n_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:wr945n:1.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-mr3020_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:tl-mr3020:1.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-mr3220_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:tl-mr3220:2.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:mr3420_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:mr3420:2.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:mr3420:3.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:wa701nd_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:wa701nd:2.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:wa801nd_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:wa801nd:3.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:wa801nd:4.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:archer_c5_firmware:*:*:*:*:*:*:*:* versions from (including) 2_150130 up to (excluding) 2_260429 OR cpe:2.3:h:tp-link:archer_c5:2.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:archer_c7_firmware:*:*:*:*:*:*:*:* versions from (including) 2_131217 up to (excluding) 2_241108 OR cpe:2.3:h:tp-link:archer_c7:2.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:archer_c7_firmware:3_150508:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:archer_c7:3.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:archer_c1900_firmware:*:*:*:*:*:*:*:* versions up to (excluding) 1_260428 OR cpe:2.3:h:tp-link:archer_c1900:1.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-wr902ac_firmware:1_160905:*:*:*:*:*:*:* *cpe:2.3:o:tp-link:tl-wr902ac_firmware:1_170628:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:tl-wr902ac:1:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-wr940n_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:tl-wr940n:4.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:tl-wr940n:2.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:tl-wr940n:v3:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-wr940n_firmware:*:*:*:*:*:*:*:* versions from (including) 5_161019 up to (including) 5_220801 OR cpe:2.3:h:tp-link:tl-wr940n:5.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-wr940n_firmware:*:*:*:*:*:*:*:* versions from (including) 6_170325 up to (excluding) 6_250925 OR cpe:2.3:h:tp-link:tl-wr940n:v6:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-wr940n_plus_firmware:6_170704:*:*:*:*:*:*:* *cpe:2.3:o:tp-link:tl-wr940n_plus_firmware:6_171115:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:tl-wr940n_plus:6.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:wr941hp_firmware:*:*:*:*:*:*:*:* versions up to (excluding) 1_211210 OR cpe:2.3:h:tp-link:wr941hp:1.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-wr941nd_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:tl-wr941nd:v5:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-wr941nd_firmware:*:*:*:*:*:*:*:* versions from (including) 6_150206 up to (excluding) 6_220610 OR cpe:2.3:h:tp-link:tl-wr941nd:v6:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:wa901nd_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:wa901nd:3.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:wa901nd_firmware:5_160929:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:wa901nd:5.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:wa901nd_firmware:*:*:*:*:*:*:*:* versions from (including) 6_191127 up to (excluding) 6_220701 OR cpe:2.3:h:tp-link:wa901nd:6.0:*:*:*:*:*:*:* Added CPE Configuration AND OR *cpe:2.3:o:tp-link:wa901nd_firmware:*:*:*:*:*:*:*:* versions from (including) 4_151029 up to (excluding) 4_201030 OR cpe:2.3:h:tp-link:wa901nd:4.0:*:*:*:*:*:*:* Changed CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-wr841n_firmware:3.16.9:build_200409:*:*:*:*:*:* OR cpe:2.3:h:tp-link:tl-wr841n:12:*:*:*:*:*:*:* AND OR *cpe:2.3:o:tp-link:tl-wr841n_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:tl-wr841n:10:*:*:*:*:*:*:* cpe:2.3:h:tp-link:tl-wr841n:8.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:tl-wr841n:9:*:*:*:*:*:*:* Changed CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-wr841n_firmware:3.16.9:build_200409:*:*:*:*:*:* OR cpe:2.3:h:tp-link:tl-wr841n:12:*:*:*:*:*:*:* AND OR *cpe:2.3:o:tp-link:tl-wr841n_firmware:-:*:*:*:*:*:*:* OR cpe:2.3:h:tp-link:tl-wr841n:10:*:*:*:*:*:*:* cpe:2.3:h:tp-link:tl-wr841n:8.0:*:*:*:*:*:*:* cpe:2.3:h:tp-link:tl-wr841n:9:*:*:*:*:*:*:* Added Reference Type Zero Day Initiative: https://www.tp-link.com/us/support/faq/5058/ Types: Vendor Advisory -
CVE Modified by 134c704f-9b21-4f2e-91b3-4a467353bcc0
Sep. 02, 2026
Action Type Old Value New Value Added Reference https://www.cisa.gov/known-exploited-vulnerabilities-catalog?field_cve=CVE-2023-50224 Removed Reference https://www.cisa.gov/known-exploited-vulnerabilities-catalog?field_cve=CVE-2023-50224 Removed Reference Type https://www.cisa.gov/known-exploited-vulnerabilities-catalog?field_cve=CVE-2023-50224 Types: US Government Resource -
CVE Modified by [email protected]
Sep. 02, 2026
Action Type Old Value New Value Changed Description TP-Link TL-WR841N dropbearpwd Improper Authentication Information Disclosure Vulnerability. This vulnerability allows network-adjacent attackers to disclose sensitive information on affected installations of TP-Link TL-WR841N routers. Authentication is not required to exploit this vulnerability. The specific flaw exists within the httpd service, which listens on TCP port 80 by default. The issue results from improper authentication. An attacker can leverage this vulnerability to disclose stored credentials, leading to further compromise. . Was ZDI-CAN-19899. TP-Link TL-WR841N dropbearpwd Improper Authentication Information Disclosure Vulnerability. This vulnerability allows network-adjacent attackers to disclose sensitive information on affected installations of TP-Link TL-WR841N routers. Authentication is not required to exploit this vulnerability. The specific flaw exists within the httpd service, which listens on TCP port 80 by default. The issue results from improper authentication. An attacker can leverage this vulnerability to disclose stored credentials, leading to further compromise. Was ZDI-CAN-19899. Added CVSS V3.1 AV:A/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N Removed CVSS V3 AV:A/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N Added Affected Affected value modified. <a href="https://github.com/CVEProject/cvelistV5/blob/main/cves/2023/50xxx/CVE-2023-50224.json">CVE-2023-50224</a> Added Reference https://www.tp-link.com/en/support/download/tl-wr841n/v12/#Firmware Added Reference https://www.tp-link.com/us/support/faq/5058/ Added Reference https://www.zerodayinitiative.com/advisories/ZDI-23-1808/ Removed Reference https://www.tp-link.com/en/support/download/tl-wr841n/v12/#Firmware Removed Reference https://www.zerodayinitiative.com/advisories/ZDI-23-1808/ Removed Reference Type https://www.tp-link.com/en/support/download/tl-wr841n/v12/#Firmware Types: Product Removed Reference Type https://www.zerodayinitiative.com/advisories/ZDI-23-1808/ Types: Third Party Advisory -
CVE Modified by af854a3a-2127-422b-91ae-364da2661108
Sep. 02, 2026
Action Type Old Value New Value Added Reference https://www.tp-link.com/en/support/download/tl-wr841n/v12/#Firmware Added Reference https://www.zerodayinitiative.com/advisories/ZDI-23-1808/ Removed Reference https://www.tp-link.com/en/support/download/tl-wr841n/v12/#Firmware Removed Reference https://www.zerodayinitiative.com/advisories/ZDI-23-1808/ Removed Reference Type https://www.tp-link.com/en/support/download/tl-wr841n/v12/#Firmware Types: Product Removed Reference Type https://www.zerodayinitiative.com/advisories/ZDI-23-1808/ Types: Third Party Advisory -
CVE Modified by [email protected]
Jun. 17, 2026
Action Type Old Value New Value Added Affected [{'vendor': 'TP-Link', 'product': 'TL-WR841N', 'versions': [{'status': 'affected', 'version': '3.16.9 build 200409'}], 'defaultStatus': 'unknown'}] -
CVE Modified by 134c704f-9b21-4f2e-91b3-4a467353bcc0
Jun. 17, 2026
Action Type Old Value New Value Added Affected [{'cpes': ['cpe:2.3:o:tp-link:tl-wr841n_firmware:-:*:*:*:*:*:*:*'], 'vendor': 'tp-link', 'product': 'tl-wr841n_firmware', 'versions': [{'status': 'affected', 'version': '0', 'lessThan': '12.0', 'versionType': 'custom'}], 'defaultStatus': 'unknown'}] Added SSVC {'id': 'CVE-2023-50224', 'role': 'CISA Coordinator', 'options': [{'exploitation': 'active'}, {'automatable': 'no'}, {'technicalImpact': 'partial'}], 'version': '2.0.3', 'timestamp': '2025-09-03T03:55:22.977218Z'} -
Modified Analysis by [email protected]
Oct. 27, 2025
Action Type Old Value New Value Added Reference Type CISA-ADP: https://www.cisa.gov/known-exploited-vulnerabilities-catalog?field_cve=CVE-2023-50224 Types: US Government Resource -
CVE Modified by 134c704f-9b21-4f2e-91b3-4a467353bcc0
Oct. 21, 2025
Action Type Old Value New Value Added Reference https://www.cisa.gov/known-exploited-vulnerabilities-catalog?field_cve=CVE-2023-50224 -
CVE Modified by 134c704f-9b21-4f2e-91b3-4a467353bcc0
Oct. 21, 2025
Action Type Old Value New Value Removed Reference https://www.cisa.gov/known-exploited-vulnerabilities-catalog?field_cve=CVE-2023-50224 -
CVE Modified by 134c704f-9b21-4f2e-91b3-4a467353bcc0
Oct. 21, 2025
Action Type Old Value New Value Added Reference https://www.cisa.gov/known-exploited-vulnerabilities-catalog?field_cve=CVE-2023-50224 -
CVE CISA KEV Update by 9119a7d8-5eab-497f-8521-727c672e3725
Sep. 04, 2025
Action Type Old Value New Value Added Date Added 2025-09-03 Added Due Date 2025-09-24 Added Required Action Apply mitigations per vendor instructions, follow applicable BOD 22-01 guidance for cloud services, or discontinue use of the product if mitigations are unavailable. Added Vulnerability Name TP-Link TL-WR841N Authentication Bypass by Spoofing Vulnerability -
Initial Analysis by [email protected]
Aug. 07, 2025
Action Type Old Value New Value Added CPE Configuration AND OR *cpe:2.3:o:tp-link:tl-wr841n_firmware:3.16.9:build_200409:*:*:*:*:*:* OR cpe:2.3:h:tp-link:tl-wr841n:12:*:*:*:*:*:*:* Added Reference Type CVE: https://www.tp-link.com/en/support/download/tl-wr841n/v12/#Firmware Types: Product Added Reference Type Zero Day Initiative: https://www.tp-link.com/en/support/download/tl-wr841n/v12/#Firmware Types: Product Added Reference Type CVE: https://www.zerodayinitiative.com/advisories/ZDI-23-1808/ Types: Third Party Advisory Added Reference Type Zero Day Initiative: https://www.zerodayinitiative.com/advisories/ZDI-23-1808/ Types: Third Party Advisory -
CVE Modified by af854a3a-2127-422b-91ae-364da2661108
Nov. 21, 2024
Action Type Old Value New Value Added Reference https://www.tp-link.com/en/support/download/tl-wr841n/v12/#Firmware Added Reference https://www.zerodayinitiative.com/advisories/ZDI-23-1808/ -
CVE Modified by [email protected]
Sep. 18, 2024
Action Type Old Value New Value Changed Description TP-Link TL-WR841N dropbearpwd Improper Authentication Information Disclosure Vulnerability. This vulnerability allows network-adjacent attackers to disclose sensitive information on affected installations of TP-Link TL-WR841N routers. Authentication is not required to exploit this vulnerability. The specific flaw exists within the httpd service, which listens on TCP port 80 by default. The issue results from improper authentication. An attacker can leverage this vulnerability to disclose stored credentials, leading to further compromise. Was ZDI-CAN-19899. TP-Link TL-WR841N dropbearpwd Improper Authentication Information Disclosure Vulnerability. This vulnerability allows network-adjacent attackers to disclose sensitive information on affected installations of TP-Link TL-WR841N routers. Authentication is not required to exploit this vulnerability. The specific flaw exists within the httpd service, which listens on TCP port 80 by default. The issue results from improper authentication. An attacker can leverage this vulnerability to disclose stored credentials, leading to further compromise. . Was ZDI-CAN-19899. -
CVE Modified by [email protected]
May. 14, 2024
Action Type Old Value New Value -
CVE Received by [email protected]
May. 03, 2024
Action Type Old Value New Value Added Description TP-Link TL-WR841N dropbearpwd Improper Authentication Information Disclosure Vulnerability. This vulnerability allows network-adjacent attackers to disclose sensitive information on affected installations of TP-Link TL-WR841N routers. Authentication is not required to exploit this vulnerability. The specific flaw exists within the httpd service, which listens on TCP port 80 by default. The issue results from improper authentication. An attacker can leverage this vulnerability to disclose stored credentials, leading to further compromise. Was ZDI-CAN-19899. Added Reference Zero Day Initiative https://www.zerodayinitiative.com/advisories/ZDI-23-1808/ [No types assigned] Added Reference Zero Day Initiative https://www.tp-link.com/en/support/download/tl-wr841n/v12/#Firmware [No types assigned] Added CWE Zero Day Initiative CWE-290 Added CVSS V3 Zero Day Initiative AV:A/AC:L/PR:N/UI:N/S:U/C:H/I:N/A:N