


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 The Register
Microsoft beefs up Remote Desktop security with ... hard-to-read messages
Microsoft's update to harden Remote Desktop against phishing attacks has arrived. When users open a Remote Desktop (.rdp) file, they should now see a warning listing all requested connection settings ...

-
 CybersecurityNews
Xiongmai IP Camera Vulnerability Let Attackers Bypass Authentication and have Remote Access
Security cameras are designed to keep commercial facilities safe. However, a newly disclosed critical vulnerability in Hangzhou Xiongmai Technology’s XM530 IP Cameras is putting networks at risk. Trac ...

-
CybersecurityNews
Python Vulnerability Allows Out-of-Bounds Write on Windows Systems
A security vulnerability has been discovered in Python’s Windows asyncio implementation, allowing attackers to trigger out-of-bounds memory writes through a missing boundary check in network socket op ...

-
CybersecurityNews
Hackers Can Exploit Ollama Model Uploads to Leak Sensitive Server Data
A critical, unpatched vulnerability has been discovered in Ollama, a widely used open-source platform for running Large Language Models locally. Tracked as CVE-2026-5757, this severe memory leak allow ...
-
 cert.pl
Vulnerability in AdaptiveGRC software
Vulnerability in AdaptiveGRC software CVE ID CVE-2026-4313 Publication date 24 April 2026 Vendor C&F Product AdaptiveGRC Vulnerable versions released before December 2025. Vulnerability type (CWE) Imp ...

-
CybersecurityNews
Hackers Use Telegram Bots to Track 900+ Successful React2Shell Exploits
A newly exposed server has revealed how a threat actor used automated tools, AI assistance, and Telegram bots to silently hack into more than 900 companies around the world. The operation, built aroun ...

-
 The Cyber Express
China-Linked Cyber Actors Turn to Massive Covert Botnets to Evade Detection
A newly issued cybersecurity advisory highlights an evolution in the tactics, techniques and procedures (TTPs) employed by China-Nexus threat actors. The report, released with support from the UK Cybe ...
-
 The Hacker News
LMDeploy CVE-2026-33626 Flaw Exploited Within 13 Hours of Disclosure
A high-severity security flaw in LMDeploy, an open-source toolkit for compressing, deploying, and serving LLMs, has come under active exploitation in the wild less than 13 hours after its public discl ...
-
 Daily CyberSecurity
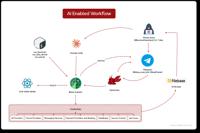
AI in the Driver’s Seat: How the ‘Bissa’ Scanner Hijacked 900+ Firms in Weeks
Image: The DFIR Report Researchers from The DFIR Report recently discovered an exposed command-and-control server that provided a rare look into a massive, AI-assisted exploitation campaign. The opera ...
-
Daily CyberSecurity
The Notification Trap: How Apple’s New iOS Patch Blocks Forensic Recovery of “Deleted” Signal Messages
Apple recently disseminated the iOS 26.4.2 update for compatible devices, primarily to remediate the vulnerability designated as CVE-2026-28950. This security flaw pertains to a method by which the FB ...