


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.

-
 Daily CyberSecurity
The Invisible Landlord: ShadowSyndicate Rotates Keys to Hide Infrastructure
Group-IB Graph analysis of the network infrastructure related to ALPHVBlackCat | Image: Group-IB The sprawling, murky network known as ShadowSyndicate has evolved. Previously identified by a singular, ...
-
Daily CyberSecurity
Popular n8n Platform Hit by Triple Threat of RCE Flaws
The n8n workflow automation platform, a favorite among technical teams for its “fair-code” flexibility and AI capabilities, has been struck by a cluster of critical security vulnerabilities. Security ...
-
Daily CyberSecurity
The Invisible Proxy: NGINX Hijacked for Silent SEO Poisoning
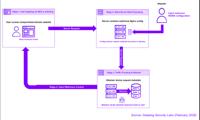
NGINX attack flow diagram showing how user requests are intercepted and routed through attacker-controlled servers | Image: Datadog Security Research A new campaign is targeting the backbone of the we ...
-
Daily CyberSecurity
4 Million Downloads at Risk: Critical Unstructured Flaw (CVSS 9.8) Allows RCE
A critical vulnerability has been discovered in the unstructured library, a powerhouse tool used by developers to prep data for Large Language Models (LLMs). With over 4 million monthly downloads, the ...
-
Daily CyberSecurity
Cloud-Hosted Trap: Phishers Use Vercel & Telegram to Bypass Filters
Social engineering attack Phishing attacks have evolved from simple “click here” links to complex, multi-stage puzzles designed to baffle security scanners. A new report from the X-Labs team uncovers ...
-
Daily CyberSecurity
“PDF” Poison: Popular JavaScript Library Patches Critical Injection and Crash Flaws
Developers using jsPDF, a widely adopted library for generating PDF files directly in the browser, are being urged to update their software immediately following the discovery of two high-severity vul ...
-
 reddit.com
Django SQL Injection in RasterField lookup (CVE-2026-1207)
Let us know your cookie preferences Reddit uses cookies and similar technologies to: Keep the website operational and running properly Prevent fraud and abuse Monitor site usage and performance metric ...
-
 Zero Day Initiative
CVE-2025-6978: Arbitrary Code Execution in the Arista NG Firewall
In this excerpt of a TrendAI Research Services vulnerability report, Jonathan Lein and Simon Humbert of the TrendAI Research team detail a recently patched command injection vulnerability in the Arist ...
-
 Help Net Security
CISA confirms exploitation of VMware ESXi flaw by ransomware attackers
CVE-2025-22225, a VMware ESXi arbitrary write vulnerability, is being used in ransomware campaigns, CISA confirmed on Wednesday by updating the vulnerability’s entry in its Known Exploited Vulnerabili ...
-
 Kaspersky
SIEM Rules for detecting exploitation of vulnerabilities in FortiCloud SSO
SIEM Kaspersky SIEM got a set of correlation rules for detecting attempts to exploit vulnerabilities for authentication bypass in Fortinet products. Igor Talankin February 5, 2026 Over the past two mo ...