


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.

-
 The Hacker News
N-able Says Attackers Take Over N-central Servers After Initial Fix Proves Incomplete
N-able said attackers exploited an authentication bypass in N-central to gain remote administrative access and reach the customer systems managed through those servers. Its first fix was incomplete. C ...
-
The Hacker News
Hugging Face Diffusers Flaws Could Let Model Repositories Execute Arbitrary Code
Three high-severity security flaws have been disclosed in Hugging Face's Diffusers library that could allow crafted model repositories to stealthily execute arbitrary code on machines that load it, op ...
-
 Huntress
Critical N-able N-central Vulnerability and Active Exploitation
Acknowledgments: Special thanks to Aaron Deal, Chris Bisnett, Aaron Bennett, Sharon Martin, Dave Kleinatland, James Northey, Josh Kiriakoff, Kamal Bennoune, and Michael Tigges for their contributions ...
-
 TheCyberThrone
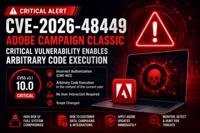
CVE-2026-48449: Critical Adobe Campaign Classic Vulnerability
IntroductionAdobe Campaign Classic (ACC) is a powerful enterprise marketing automation platform used by organizations to orchestrate customer engagement, manage large-scale marketing campaigns, and in ...
-
The Hacker News
Adobe Campaign Classic CVSS 10.0 Flaw Could Run Code Without User Interaction
Adobe has released security updates to address a maximum-severity security flaw in Campaign Classic (ACC), its enterprise-focused marketing automation platform, that could result in arbitrary code exe ...
-
TheCyberThrone
Chrome’s 1,400+ Vulnerability Wake-Up Call
How AI Is Transforming Browser Security—and Why CISOs Must Rethink Vulnerability GovernanceFor years, browser updates have been treated as routine maintenance. A notification appears, users click “Upd ...
-
 cert.pl
Vulnerabilities in PHP Jabbers scripts
Vulnerabilities in PHP Jabbers scripts CVE ID CVE-2025-67649 Publication date 31 July 2026 Vendor PHP Jabbers Product Car Rental Script Vulnerable versions All before 4.1 Vulnerability type (CWE) Impr ...
-
The Hacker News
Three Recent Chrome Releases Fix 1,442 Flaws, More Than Prior 23 Updates Combined
Google on Thursday announced that it fixed a whopping 1,072 security bugs in Chrome versions 149 and 150, surpassing the total number of flaws the company fixed across the prior 23 milestones combined ...
-
The Hacker News
Researchers Report 84 Flaws in 4G and 5G Cores, Including a Session Hijacking Flaw
An academic study has disclosed a "widespread class" of security vulnerabilities impacting 4G and 5G core networks that, if successfully exploited, could trigger denial-of-service (DoS) attacks and ev ...
-
The Hacker News
Chinese Hacker Commands DeepSeek via Telegram to Launch Autonomous Attacks
Palo Alto Networks' Unit 42 says a Chinese-speaking threat actor used DeepSeek through the open-source Hermes Agent framework to launch attacks autonomously. After an initial Telegram instruction, the ...