


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 Daily CyberSecurity
GlassWorm Supply Chain Worm Uses Invisible Unicode and Solana Blockchain for Stealth C2
Cybersecurity researchers at Koi Security have discovered the world’s first self-propagating malware targeting VS Code extensions on the OpenVSX Marketplace. Dubbed GlassWorm, the threat marks a histo ...
-
Daily CyberSecurity
Critical Moxa Flaw (CVE-2025-6950, CVSS 9.9) Allows Unauthenticated Admin Takeover via Hard-Coded JWT Secret
Moxa, a leading manufacturer of industrial networking and security appliances, has released an urgent security advisory addressing five critical vulnerabilities affecting multiple product series, incl ...
-
Daily CyberSecurity
Critical Keras 3 RCE Flaw (CVE-2025-49655, CVSS 9.8) Allows Code Execution on Model Load
Researchers at HiddenLayer have disclosed a critical arbitrary code execution vulnerability in the Keras 3 deep learning framework (CVE-2025-49655, CVSS 9.8), which affects the Torch backend of Keras ...
-
 CybersecurityNews
PoC Exploit Released for Linux-PAM Vulnerability Allowing Root Privilege Escalation
A high-severity vulnerability in the Pluggable Authentication Modules (PAM) framework was assigned the identifier CVE-2025-8941. This vulnerability stems from the heart of Linux operating systems, ena ...

-
CybersecurityNews
WatchGuard VPN Vulnerability Let Remote Attacker Execute Arbitrary Code
WatchGuard has disclosed a critical out-of-bounds write vulnerability in its Fireware OS, enabling remote unauthenticated attackers to execute arbitrary code via IKEv2 VPN connections. Designated CVE- ...
-
 Help Net Security
Week in review: F5 data breach, Microsoft patches three actively exploited zero-days
Here’s an overview of some of last week’s most interesting news, articles, interviews and videos: Building a healthcare cybersecurity strategy that works In this Help Net Security interview, Wayman Cu ...
-
 seclists.org
CyberDanube Security Research 20251014-0 | Multiple Vulnerabilities in Phoenix Contact QUINT4 UPS
Full Disclosure mailing list archives CyberDanube Security Research 20251014-0 | Multiple Vulnerabilities in Phoenix Contact QUINT4 UPS From: Thomas Weber | CyberDanube via Fulldisclosure <fulldisclos ...
-
CybersecurityNews
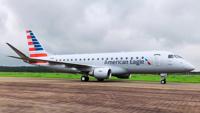
American Airlines Subsidiary Envoy Compromised in Oracle Hacking Campaign
Envoy Air, a wholly owned subsidiary of American Airlines, has confirmed it fell victim to a hacking campaign exploiting vulnerabilities in Oracle’s E-Business Suite (EBS). The breach, first highlight ...
-
 TheCyberThrone
Inside the F5 BIG-IP 2025 Security Incident: Source Code Theft and Urgent Patch Release
OverviewIn October 2025, F5 Networks disclosed a significant cybersecurity incident involving a sophisticated nation-state threat actor who breached its corporate networks. This breach, detected initi ...

-
CybersecurityNews
PoC Exploit Released for 7-Zip Vulnerabilities that Let Attackers Execute Arbitrary Code Remotely
A proof-of-concept exploit for two critical vulnerabilities in the popular file archiver 7-Zip, potentially allowing attackers to execute arbitrary code remotely through malicious ZIP files. The flaws ...