


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 Daily CyberSecurity
The Browser War Heats Up: OpenAI Unveils AI-Powered ChatGPT Atlas
As the battle for dominance in the AI browser arena intensifies, OpenAI has officially unveiled its AI-powered web browser, ChatGPT Atlas—a bold move aimed at challenging Google’s reign as the primary ...
-
Daily CyberSecurity
Chrome Update: New High-Severity Flaw in V8 Engine (CVE-2025-12036) Requires Immediate Patch
Google has released a Stable Channel update (version 141.0.7390.122/.123) for Windows, Mac, and Linux, addressing a high-severity vulnerability in the V8 JavaScript engine — the core component respons ...
-
Daily CyberSecurity
Critical Sauter AG Flaw (CVE-2025-41723, CVSS 9.8) Allows Unauthenticated File Upload via SOAP Interface
Swiss building automation manufacturer Sauter AG has disclosed six vulnerabilities in the embedded firmware of its modulo 6 devices, warning that attackers could exploit these flaws to gain remote con ...
-
Daily CyberSecurity
Critical ABB Flaw (CVE-2025-9574, CVSS 9.9) Exposes EoL Load Controllers to Unauthenticated Admin Access
Industrial automation giant ABB has disclosed a critical missing authentication vulnerability (CVE-2025-9574) affecting its ALS-mini-S4/S8 IP intelligent load controllers, which are deployed in energy ...
-
Daily CyberSecurity
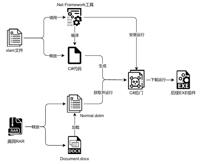
Bitter APT Attacks China/Pakistan with WinRAR Zero-Day and New C# Backdoor via Office Macro
Image: Qianxin China-based cybersecurity firm Qianxin Threat Intelligence Center has uncovered a new wave of attacks linked to the Bitter APT group (APT-Q-37), also known as 蔓灵花. The group—widely beli ...
-
Daily CyberSecurity
WSO2 Fixes Two Critical Access Control Vulnerabilities (CVE-2025-9804, CVE-2025-10611) Affecting API Manager and Identity Server
The WSO2 project has released urgent security advisories addressing two critical access control vulnerabilities—CVE-2025-9804 and CVE-2025-10611—that affect multiple enterprise products, including API ...
-
 Trend Micro
The Rise of Collaborative Tactics Among China-aligned Cyber Espionage Campaigns
Key takeaways “Premier Pass-as-a-Service” describes the emerging trend of advanced collaboration tactics between multiple China-aligned APT groups, notably Earth Estries and Earth Naga, that are makin ...
-
 BleepingComputer
TP-Link warns of critical command injection flaw in Omada gateways
TP-Link is warning of two command injection vulnerabilities in Omada gateway devices that could be exploited to execute arbitrary OS commands. Omada gateways are marketed as full-stack solutions (rout ...
-
 CrowdStrike.com
CrowdStrike Identifies Campaign Targeting Oracle E-Business Suite via Zero-Day Vulnerability (now tracked as CVE-2025-61882)
CrowdStrike is tracking a mass exploitation campaign almost certainly leveraging a novel zero-day vulnerability — now tracked as CVE-2025-61882 — targeting Oracle E-Business Suite (EBS) applications f ...
-
 The Register
MCP attack abuses predictable session IDs to hijack AI agents
A security flaw in the Oat++ implementation of Anthropic's Model Context Protocol (MCP) allows attackers to predict or capture session IDs from active AI conversations, hijack MCP sessions, and inject ...