


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 security.nl
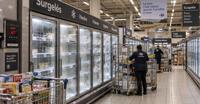
Franse overheid adviseert supermarkten om koelsystemen offline te halen
De Franse overheid adviseert supermarkten en andere bedrijven om hun koelsystemen offline te halen. In het geval van gehackte koelinstallaties wordt aangeraden om een fabrieksreset uit te voeren. Volg ...
-
 cert.pl
Vulnerability in Payload CMS software
Vulnerability in Payload CMS software CVE ID CVE-2026-63316 Publication date 13 October 2026 Vendor Payload Product Payload CMS Vulnerable versions All before 3.90.0From 4.0.0-canary.0 to 4.0.0-canary ...
-
security.nl
GitLab waarschuwt voor kritiek beveiligingslek met CVSS 10.0-score
GitLab waarschuwt ontwikkelaars en organisaties voor een kritieke kwetsbaarheid in de software die een CVSS-impactscore van 10.0 op een schaal van 1 tot en met 10 heeft. GitLab is een populaire online ...
-
 The Hacker News
Attackers Heat French Supermarket Fridges Up to 50°C by Hijacking Danfoss Controllers
Attackers took remote control of fridges and freezers at hundreds of French supermarkets on the night of October 11 and warmed them, forcing stores to throw food away, several retail chains said. The ...
-
The Hacker News
Two Critical MarkLogic Flaws Could Give Delegated Managers Persistent Admin Control
Two of 31 newly disclosed flaws in Progress Software's MarkLogic Server database could let an account given only some management privileges take administrator control of the server, the company says. ...
-
The Hacker News
GitLab Patches CVSS 10.0 Flaw That Could Let Unauthenticated Users Run Server Code
GitLab has released patches for a maximum-severity security flaw impacting its Community Edition (CE) and Enterprise Edition (EE) software that could result in arbitrary code execution. "GitLab has re ...
-
 Dark Reading
Maximum-Severity SSRF Flaw in SonicWall SMA Devices Under Attack
Rob Wright,Senior News Director,Dark ReadingOctober 12, 20264 Min ReadSource: Michael Vi via Alamy Stock PhotoSonicWall customers are on the defensive once again, as threat actors are actively exploit ...
-
The Hacker News
⚡ Weekly Recap: Helpdesk 0-Days, Rogue Certs, ShinyHunters Arrest, AI-Fooling Malware and More
Some meetings last longer than it took attackers to jump on a newly disclosed security flaw this week. Within hours, they were already testing it. That's not much time to read the warning, let alone d ...
-
 TheCyberThrone
CVE-2026-97229: Critical GitLab Vulnerability Could Allow Remote Code Execution
October 12, 2026GitLab has addressed CVE-2026-97229, a critical vulnerability in its CI/CD Regular Expression Compiler that could allow an unauthenticated attacker to execute arbitrary code on a vulne ...
-
The Hacker News
Critical SonicWall SMA 1000 Flaw Targeted in 135 Exploitation Attempts After Patch
Threat actors have been observed exploiting a recently disclosed critical security flaw in SonicWall Secure Mobile Access (SMA) 1000 appliances within days of public disclosure. The vulnerability, tra ...