


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 The Hacker News
CISA Urges Immediate Ivanti Connect Secure Updates as Honeypots Log 105 Exploit Attempts
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday urged organizations to take steps to immediately update their Ivanti Connect Secure (ICS) appliances and deployments to the ...
-
The Hacker News
curl Patches HTTP/2 Upload Flaw After PoC Demonstrates Client-Side Code Execution
A flaw in how curl handles HTTP/2 uploads lets a malicious server receiving an upload corrupt the client's memory, and the researcher who reported it turned that into code execution on the uploading m ...
-
The Hacker News
Researchers Used a Public OpenAI Model to Build a $250,000 Chrome Full-Chain Exploit in Six Days
A team at security firm XBOW chained three then-unknown Google Chrome bugs into a single attack that runs code on a Windows computer when the user only loads a web page, the company said. Its research ...
-
 security.nl
Ivanti vpn-servers volledig gehackt bij aanval, aanvallers zoeken BitLocker keys
Bij de recente aanvallen tegen Ivanti vpn-servers combineerden de aanvallers drie verschillende kwetsbaarheden om zo volledige controle over de systemen te krijgen. Vervolgens probeerden ze allerlei c ...
-
The Hacker News
AI-Found Linux Kernel Flaw Gives Local Users Root, and Can Break a Guest Out to the Host
A flaw in Linux's vhost subsystem lets a local user read and write kernel memory at will and become root across nearly a decade of kernel versions. In one virtualization setup, it lets an untrusted vi ...
-
security.nl
Microsoft dicht ruim 1400 beveiligingslekken tijdens record Patch Tuesday
Tijdens de Patch Tuesday van oktober heeft Microsoft ruim 1400 beveiligingslekken in de eigen software gepatcht, waaronder een actief aangevallen kwetsbaarheid. Niet eerder dichtte Microsoft tijdens e ...
-
The Hacker News
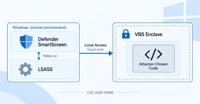
Four-Byte Write and Timing Bug Let Researchers Run Code in Windows SmartScreen Enclave
Security researchers ran their own code inside a protected part of Windows that is meant to stay sealed off even when the rest of the computer is taken over. The protected area is a VBS enclave, an is ...
-
The Hacker News
Microsoft Patches Record 1,413 Flaws, Including Exploited Windows Shell Bug
Microsoft on Tuesday shattered its own Patch Tuesday record by shipping patches for a whopping 1,413 vulnerabilities, including one that it said has come under active exploitation. These include 1,102 ...
-
 TheCyberThrone
Microsoft Patch Tuesday – October 2026
1,411 Vulnerabilities and Three Zero-DaysStudy SecurityAn actively exploited Windows Shell flaw, publicly disclosed vulnerabilities and a record-breaking security release put enterprise patch managem ...
-
 CrowdStrike.com
October 2026 Patch Tuesday: 1,413 CVEs Include Three Zero-Days and 75 Critical Vulnerabilities
Microsoft addressed 1,413 vulnerabilities in its October 2026 security update release, including one exploited zero-day vulnerability, two publicly disclosed zero-day vulnerabilities, and 75 Critical ...