


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 Daily CyberSecurity
Critical CVE-2025-1976 Vulnerability in Brocade Fabric OS Actively Exploited
A critical security vulnerability has been identified in Brocade Fabric OS, posing a significant risk to affected systems. The vulnerability, tracked as CVE-2025-1976, allows a local user with admin p ...
-
Daily CyberSecurity
RustoBot Botnet Exploits Router Flaws in Sophisticated Attacks
FortiGuard Labs recently discovered RustoBot, written in Rust, a memory-safe language known for its performance and security, a sophisticated botnet exploiting vulnerabilities in TOTOLINK and DrayTek ...
-
Daily CyberSecurity
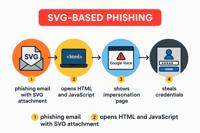
SVG Files Weaponized: Phishing Attacks Embed HTML Code
Phishing is no longer just about shady links and poorly worded emails. According to a new report from Kaspersky Labs, threat actors are now embedding HTML and JavaScript code inside SVG files—turning ...
-
Daily CyberSecurity
Over 50k WordPress Sites at Takeover Risk Via Vulnerable Plugin
A critical vulnerability affecting the popular WordPress plugin Greenshift – animation and page builder blocks has come to light, potentially placing over 50,000 active websites at risk of full compro ...
-
 The Register
Today's LLMs craft exploits from patches at lightning speed
The time from vulnerability disclosure to proof-of-concept (PoC) exploit code can now be as short as a few hours, thanks to generative AI models. Matthew Keely, of Platform Security and penetration te ...
-
 Cyber Security News
Microsoft Addresses Entra ID Token Logging Issue, Alerts to Protect Users
Microsoft has acknowledged a recent issue that triggered widespread alerts in its Entra ID Protection system, flagging user accounts as high risk due to supposed credential leaks on the dark web. The ...
-
The Register
Microsoft rated this bug as low exploitability. Miscreants weaponized it in just 8 days
On March 11 - Patch Tuesday - Microsoft rolled out its usual buffet of bug fixes. Just eight days later, miscreants had weaponized one of the vulnerabilities, using it against government and private s ...
-
 The Hacker News
Kimsuky Exploits BlueKeep RDP Vulnerability to Breach Systems in South Korea and Japan
Cybersecurity researchers have flagged a new malicious campaign related to the North Korean state-sponsored threat actor known as Kimsuky that exploits a now-patched vulnerability impacting Microsoft ...
-
 Dark Reading
ASUS Urges Users to Patch AiCloud Router Vuln Immediately
Source: A_Gree via Alamy Stock PhotoNEWS BRIEFASUS recently disclosed a critical security vulnerability affecting routers that have AiCloud enabled, potentially allowing remote attackers to perform un ...
-
Cyber Security News
RedGolf Hackers Expose Fortinet Exploits & Tools Used to Hack Organizations
RedGolf, a sophisticated threat actor with ties to APT41, provided a rare insight into its operational toolbox after a directory on their attack infrastructure was briefly exposed. The server, linked ...