


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 seclists.org
IBMi Navigator / CVE-2024-51464 / HTTP Security Token Bypass
Full Disclosure mailing list archives IBMi Navigator / CVE-2024-51464 / HTTP Security Token Bypass From: hyp3rlinx <apparitionsec () gmail com> Date: Fri, 27 Dec 2024 22:21:21 -0500 [+] Credits: John ...
-
seclists.org
IBMi Navigator / CVE-2024-51463 / Server Side Request Forgery (SSRF)
Full Disclosure mailing list archives IBMi Navigator / CVE-2024-51463 / Server Side Request Forgery (SSRF) From: hyp3rlinx <apparitionsec () gmail com> Date: Fri, 27 Dec 2024 22:19:52 -0500 [+] Credit ...
-
 TheCyberThrone
CISA adds PaloAlto CVE-2024-3393 to its KEV Catalog
The Cybersecurity and Infrastructure Security Agency (CISA) recently added CVE-2024-3393 to its Known Exploited Vulnerabilities (KEV) Catalog. This vulnerability affects Palo Alto Networks’ PAN-OS sof ...
-
 Cybersecurity News
CISA Warns of Actively Exploited Palo Alto Firewall Flaw (CVE-2024-3393)
The Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent warning about an actively exploited vulnerability in Palo Alto Networks PAN-OS firewall software. This critical flaw, t ...
-
Cybersecurity News
CVE-2024-11944: TrueNAS CORE Vulnerability Allows Unauthenticated Attacks
A critical vulnerability has been uncovered in TrueNAS CORE, the popular open-source network-attached storage (NAS) operating system. Tracked as CVE-2024-11944 and assigned a CVSS score of 7.5, this s ...
-
Cybersecurity News
66,000 DrayTek Gateways Vulnerable to Remote Command Injection (CVE-2024-12987), PoC Published
Security researcher Netsecfish has discovered a command injection vulnerability, tracked as CVE-2024-12987, in the web management interface of popular DrayTek gateway devices. This flaw could enable a ...
-
Cybersecurity News
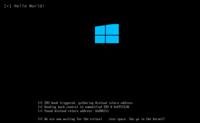
Stealthy UEFI Bootkit Targets Windows Kernel, Raising Security Concerns
Security researchers NSG650 and Pdawg have unveiled a proof-of-concept UEFI bootkit that exploits a critical firmware function to compromise the Windows kernel during the boot process. This bootkit de ...
-
Cybersecurity News
IBM’s HashiCorp Acquisition Under Scrutiny: CMA Investigates Competition Concerns
The United Kingdom’s Competition and Markets Authority (CMA) recently announced that it would launch an investigation into IBM’s $6.4 billion acquisition of HashiCorp, a software company specializing ...
-
 Huntress
2024: Revisiting a Year in Threats | Huntress
Before you pop the bubbly and count down to a new year, let’s reminisce for a moment. Looking back on the past 365 days, it was clear cybercriminals had no intention of slowing down. But neither did w ...
-
 BleepingComputer
US Treasury Department breached through remote support platform
Chinese state-sponsored threat actors hacked the U.S. Treasury Department after breaching a remote support platform used by the federal agency. In a letter sent to lawmakers and seen by the New York T ...