


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.

-
 TheCyberThrone
CISA added Veeam Backup CVE-2024-40711 to its KEV Catalog
The US CISA has added Veeam Backup flaw to its Known Exploited Vulnerabilities Catalog based on the evidence of active exploitation.CVE-2024-40711 Veeam Backup and Replication contains a deserializati ...
-
 Cybersecurity News
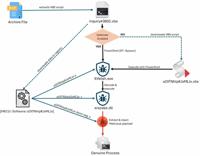
HORUS Protector: The New Undetectable Malware Crypter Threatening Cybersecurity
In a recent discovery by the SonicWall Capture Labs threat research team, a new malware crypter known as “HORUS Protector” has emerged, presenting a significant threat to cybersecurity defenses. This ...
-
Cybersecurity News
Cisco ATA 190 Series Analog Telephone Adapter Firmware Flaws Exposed: Patch Now!
Cisco has recently disclosed a series of high-severity vulnerabilities in the Cisco ATA 190 Series Analog Telephone Adapter firmware, including both on-premises and multiplatform variants. These vulne ...
-
Cybersecurity News
HM Surf (CVE-2024-44133): macOS Flaw Exposing Cameras and Microphones to Hackers, PoC Published
In a significant discovery by Microsoft Threat Intelligence, a vulnerability in macOS, identified as CVE-2024-44133, has been found to bypass Apple’s Transparency, Consent, and Control (TCC) technolog ...
-
TheCyberThrone
VMware fixes CVE-2024-38814 in HCX
Broadcom disclosed a SQL injection vulnerability affecting VMware HCX, a key component used in multi-cloud infrastructures to enable application migration and disaster recovery.The vulnerability track ...
-
 The Cyber Express
GitHub Issues Urgent Security Advisory on Critical Vulnerability in GitHub Enterprise Server
GitHub has released a critical security advisory highlighting vulnerabilities that merit immediate action from users of GitHub Enterprise Server (GHES). The advisory focuses on a GitHub vulnerability ...

-
 Krypt3ia
Comprehensive Threat Intelligence Report: The Rise of Nation-State Cyber Attacks and Their Convergence with Cybercrime
TLP: WHITE This threat intelligence report was written in tandem between Krypt3ia and the ICEBREAKER Threat Intelligence Analyst created by Krypt3ia. Executive Summary Over the past year, nation-state ...
-
Cybersecurity News
CVE-2024-43240 & CVE-2024-43242 in Ultimate Membership Pro Plugin Put 40,000 Websites at Risk
The Ultimate Membership Pro plugin, a premium WordPress plugin widely used for managing membership subscriptions, has been found to contain two critical vulnerabilities, according to a report from Raf ...

-
 The Hacker News
SideWinder APT Strikes Middle East and Africa With Stealthy Multi-Stage Attack
An advanced persistent threat (APT) actor with suspected ties to India has sprung forth with a flurry of attacks against high-profile entities and strategic infrastructures in the Middle East and Afri ...
-
 Kaspersky
SAS CTF and the many ways to persist a kernel shellcode on Windows 7
SAS 17 Oct 2024 16 minute read On May 18, 2024, Kaspersky’s Global Research & Analysis Team (GReAT), with the help of its partners, held the qualifying stage of the SAS CTF, an international competiti ...