


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 Daily CyberSecurity
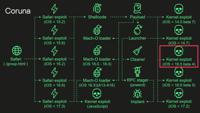
The Return of Operation Triangulation: Coruna Exploit Kit Targets M3 and A17 Chips in Massive iOS Offensive
Attack chain of Coruna | Image: Kaspersky Labs On March 4, 2026, reports from Google and iVerify shed light on Coruna, a highly sophisticated exploit kit targeting Apple iPhones. While such advanced t ...
-
 europa.eu
Cyber Brief 26-04 - March 2026
Cyber Brief (March 2026)April 1, 2026 – Version: 1TLP:CLEARExecutive summaryWe analysed 343 open source reports for this Cyber Brief1.Relating to cyber policy and law enforcement, the Council of the E ...
-
Daily CyberSecurity
Ghost in the Drone: Unauthenticated Shell Access in PX4 Autopilot’s 9.8 CVSS Nightmare
A critical security advisory has been issued for the PX4 Autopilot system. The vulnerability, tracked as CVE-2026-1579, carries a CVSS score of 9.8, highlighting a “nightmare scenario” for unhardened ...
-
Daily CyberSecurity
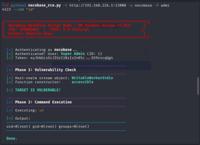
NocoBase Critical Alert: Sandbox Escape Grants Attackers Root Access
A critical vulnerability has been unearthed in NocoBase, the AI-powered platform designed for infinite extensibility. The flaw, tracked as CVE-2026-34156, carries a maximum CVSS score of 10, indicatin ...
-
Daily CyberSecurity
ASUS Issues Security Patch for Router Vulnerability
In a move to fortify home and office networks, ASUS has released a security update for several of its router models. The update targets a high-severity vulnerability that could allow attackers to hija ...
-
 security.nl
Google rolt update uit voor actief aangevallen beveiligingslek in Chrome
Google heeft een update voor een actief aangevallen beveiligingslek in Chrome uitgerold. De kwetsbaarheid (CVE-2026-5281) bevindt zich in Dawn, een open source en crossplatform implementatie van de We ...

-
 CybersecurityNews
Hackers Actively Exploiting Critical WebLogic RCE Vulnerabilities in Attacks
A recent cybersecurity study reveals that threat actors are moving faster than ever to weaponize new software flaws. According to data collected from a high-interaction honeypot, hackers are actively ...

-
CybersecurityNews
New Chrome Zero-Day Vulnerability Actively Exploited in Attacks — Patch Now
Google has released an emergency security update for its Chrome browser, patching a zero-day vulnerability that is already being actively exploited in the wild. The Stable channel has been updated to ...
-
Daily CyberSecurity
2 Million Monthly Users at Risk: Critical 9.3 CVSS SQL Injection Hits MikroORM in “Duck-Typed” Disaster
A critical vulnerability has been identified in MikroORM, a widely used TypeScript Object-Relational Mapper (ORM) for Node.js. With over 2 million downloads every month, the impact of this flaw could ...
-
 The Hacker News
New Chrome Zero-Day CVE-2026-5281 Under Active Exploitation — Patch Released
Google on Thursday released security updates for its Chrome web browser to address 21 vulnerabilities, including a zero-day flaw that it said has been exploited in the wild. The high-severity vulnerab ...