


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 CybersecurityNews
PoC Exploit Released for ImageMagick RCE Vulnerability – Update Now
A proof-of-concept (PoC) exploit has been released for a critical remote code execution (RCE) vulnerability in ImageMagick 7’s MagickCore subsystem, specifically affecting the blob I/O (BlobStream) im ...
-
 The Register
CISA sounds alarm over TP-Link wireless routers under attack
Infosec in brief The US Cybersecurity and Infrastructure Security Agency (CISA) has said two flaws in routers made by Chinese networking biz TP-Link are under active attack and need to be fixed – but ...
-
 cert.pl
Vulnerability in ITCube CRM software
Vulnerability in ITCube CRM software CVE ID CVE-2025-5993 Publication date 08 September 2025 Vendor ITCube Software Product ITCube CRM Vulnerable versions From 2023.2 through 2025.2 Vulnerability type ...
-
 The Cyber Express
Pakistan Launches Probe After Massive SIM Data Leak Hits Millions
The Pakistani government has launched an urgent investigation following reports of a massive data leak involving SIM holders’ personal information, including that of Interior Minister Mohsin Naqvi. Th ...
-
 nextron-systems.com
Detecting NetScaler Compromise with THOR During CVE-2025-7775 Attacks
Citrix NetScaler appliances are once again the target of active exploitation. On August 26, 2025, Citrix published a security advisory CTX694938 describing three critical vulnerabilities. Most notably ...
-
The Cyber Express
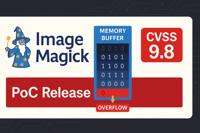
Argo CD Security Flaw Rated 9.8 Leaves GitOps Repositories Exposed
A security flaw in Argo CD, the popular open-source GitOps tool for Kubernetes, has been targeted at the DevOps and cloud-native communities. Tracked as CVE-2025-55190, the vulnerability has been rate ...
-
 Daily CyberSecurity
CVE-2025-57807: A Critical Flaw in ImageMagick Could Lead to RCE, PoC Available
Security researcher Lumina Mescuwa has disclosed a critical vulnerability in ImageMagick, tracked as CVE-2025-57807 (CVSS 9.8). The flaw stems from a contract mismatch in BlobStream’s SeekBlob() and W ...
-
Daily CyberSecurity
Microsoft Access 2016/2019 Is Nearing End-of-Life
A wide range of Microsoft products will reach the end of their lifecycle in October 2025. Alongside Windows 10, Microsoft’s relational database application Microsoft Access 2016/2019 will officially l ...
-
Daily CyberSecurity
CVE-2025-58782: Apache Jackrabbit Vulnerability Exposes Systems to JNDI Injection and RCE
The Apache Software Foundation has disclosed a new vulnerability in Apache Jackrabbit Core and JCR Commons, tracked as CVE-2025-58782. The flaw, classified as Important, impacts versions 1.0.0 through ...
-
Daily CyberSecurity
Progress Patches Remote Command Execution Flaw in OpenEdge AdminServer (CVE-2025-7388)
Progress Software has released patches for a high-severity vulnerability in the OpenEdge AdminServer component, tracked as CVE-2025-7388 (CVSS 8.4). The flaw affects OpenEdge LTS Releases 12.2.17, 12. ...