


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 The Hacker News
JADEPUFFER-Linked Attackers Used Compromised Service Principals to Delete Azure Resources
The threat actor known as JADEPUFFER has been observed orchestrating destructive actions within a Microsoft Azure environment using compromised service principals. Microsoft, which is tracking the act ...
-
 security.nl
Citrix waarschuwt voor misbruikte kwetsbaarheden: 'Zo snel mogelijk updaten'
Citrix waarschuwt voor twee kritieke kwetsbaarheden in Citrix NetScaler ADC en Gateway waar aanvallers actief misbruik van maken. Patches zijn nu beschikbaar gesteld, maar het misbruik vond al voor he ...
-
The Hacker News
CISA Says Attackers Are Exploiting Two Critical Citrix NetScaler Flaws Globally
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Sunday added two critical Citrix NetScaler ADC and Gateway flaws to its Known Exploited Vulnerabilities (KEV) catalog, following rep ...
-
 TheCyberThrone
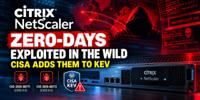
Citrix NetScaler Zero-Days Exploited in the Wild: CISA Adds Them to KEV
Executive SummaryCitrix has confirmed that two NetScaler ADC and NetScaler Gateway zero-day vulnerabilities — CVE-2026-88771 and CVE-2026-88772 — are being exploited in the wild.Both are rated CVSS 9. ...
-
The Hacker News
Warning: Two Unpatched Citrix NetScaler RCE Zero-Days Under Active Exploitation
Two new unpatched zero-day vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway appliances that allow remote code execution are being actively exploited in the wild, security firm watchTowr s ...
-
The Hacker News
Lunex Stealer Abuses AMD Driver to Disable Security Monitoring and Steal Browser Credentials
The Psychedelic Stealer malware distributed via compromised Ukrainian websites using ClickFix-style Cloudflare verification checks is part of a wider malware-as-a-service (MaaS) platform called Lunex. ...
-
The Hacker News
Attackers Bypass WAFs to Exploit Oracle PeopleSoft Flaw and Deploy Web Shells
Google is warning of renewed mass exploitation of a known security vulnerability in Oracle PeopleSoft as part of a campaign targeting multiple sectors globally. The ShinyHunters-linked activity involv ...
-
The Hacker News
SharePoint RCE and MikroTik RouterOS Flaws Actively Exploited in the Wild
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added two security flaws impacting Microsoft SharePoint and Mikrotik RouterOS to its Known Exploited Vulnerabilities (KEV) ca ...
-
 Kaspersky
CVE-2026-87902: Critical Vulnerability in WordPress
vulnerability CVE-2026-87902, a new critical vulnerability in the WordPress core, is already being actively exploited in real-world attacks. Editorial Team September 25, 2026 A critical vulnerability ...
-
security.nl
Roundcube Webmail SQL Injection-lek misbruikt bij aanvallen
Een SQL Injection-kwetsbaarheid in Roundcube wordt misbruikt bij aanvallen. Dat laat het Canadese Centrum voor Cybersecurity weten. Roundcube is opensource-webmailsoftware en wordt door allerlei organ ...