


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 seclists.org
Dovecot CVE-2024-23185: Very large headers can cause resource exhaustion when parsing message
Full Disclosure mailing list archives From: Aki Tuomi via Fulldisclosure <fulldisclosure () seclists org> Date: Wed, 14 Aug 2024 14:13:42 +0300 (EEST) Affected product: Dovecot IMAP Server Internal re ...
-
seclists.org
CVE-2024-23184: Having a large number of address headers (From, To, Cc, Bcc, etc.) becomes excessively CPU intensive
Full Disclosure mailing list archives From: Aki Tuomi via Fulldisclosure <fulldisclosure () seclists org> Date: Wed, 14 Aug 2024 14:13:42 +0300 (EEST) Affected product: Dovecot IMAP Server Internal re ...
-
 Cybersecurity News
10,000+ WordPress Sites at Risk: Critical File Deletion Flaw Found in InPost Plugins
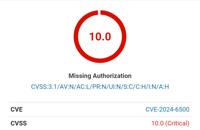
A critical vulnerability, tracked as CVE-2024-6500 (CVSS 10), has been uncovered in two popular WordPress plugins, InPost PL and InPost for WooCommerce, leaving over 10,000 websites susceptible to com ...
-
Cybersecurity News
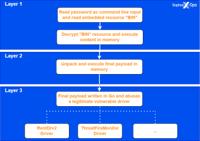
EDRKillShifter: A New EDR-Killing Tool in Ransomware Attack
High-level overview of the loader execution process | Image: SophosSophos researchers have discovered a new threat: EDRKillShifter, a sophisticated tool designed to dismantle endpoint detection and re ...
-
Cybersecurity News
Cybercriminals Evolve Social Engineering Tactics, Exploit CVE-2022-26923 in Sophisticated Campaign
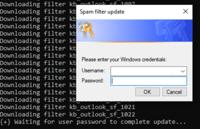
Credential harvester prompt spawned by `AntiSpam.exe | Image: Rapid7 Recently, cybersecurity firm Rapid7 identified a series of sophisticated intrusion attempts linked to an ongoing social engineering ...

-
 Cyber Security News
Windows 0-Day Flaw Exploited by Lazarus to Gain Unauthorized Access
Security researchers at Avast have uncovered evidence that the notorious North Korean hacker group Lazarus exploited a previously unknown zero-day vulnerability in the Windows AFD.sys driver to gain k ...
-
 The Cyber Express
Copy2Pwn Vulnerability Bypasses Windows Protections
Security experts recently uncovered a vulnerability, CVE-2024-38213, that allows threat actors to bypass Windows’ Mark-of-the-Web (MotW) protections through copy-and-paste operations. This vulnerabili ...

-
The Cyber Express
Weekly Vulnerability Report: Cyble Urges Fixes in SAP, Ivanti, AMD and More
Between the Black Hat and DEF CON conferences and Patch Tuesday, it’s been a very busy week for security vulnerabilities. Cyble researchers investigated 40 vulnerabilities in their Aug. 7-13 report fo ...

-
 BleepingComputer
CISA warns critical SolarWinds RCE bug is exploited in attacks
Image: MidjourneyCISA warned on Thursday that attackers are exploiting a recently patched critical vulnerability in SolarWinds' Web Help Desk solution for customer support. Web Help Desk (WHD) is IT h ...
-
 TheCyberThrone
CISA Adds Solarwinds CVE-2024-28986 to KEV Catalog
The U.S.CISA warned of a critical security vulnerability affecting SolarWinds Web Help Desk.This vulnerability, tracked as CVE-2024-28986 with a CVSS 9.8, has been added to CISA’s Known Exploited Vuln ...