


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 The Cyber Express
Critical ICS Vulnerabilities Discovered in Schneider Electric, mySCADA, and Automated Logic Products
A recent Cyble ICS vulnerabilities report sheds light on several critical vulnerabilities in industrial control systems (ICS) from major vendors including Schneider Electric, mySCADA, and Automated Lo ...
-
 Kaspersky
IT threat evolution in Q3 2024. Non-mobile statistics
IT threat evolution in Q3 2024 IT threat evolution in Q3 2024. Non-mobile statistics IT threat evolution in Q3 2024. Mobile statistics The statistics presented here are based on detection verdicts by ...

-
Kaspersky
IT threat evolution Q3 2024
IT threat evolution in Q3 2024 IT threat evolution in Q3 2024. Non-mobile statistics IT threat evolution in Q3 2024. Mobile statistics Targeted attacks New APT threat actor targets Russian government ...
-
 The Hacker News
Microsoft Fixes AI, Cloud, and ERP Security Flaws; One Exploited in Active Attacks
AI Security / Cloud Security Microsoft has addressed four security flaws impacting its artificial intelligence (AI), cloud, enterprise resource planning, and Partner Center offerings, including one th ...
-
The Cyber Express
Zyxel Firewalls Targeted by Helldown Ransomware: CVE-2024-11667 Exploited
Zyxel Firewalls have become a key target in recent cyberattacks, with attackers exploiting a critical vulnerability to deploy the dangerous Helldown ransomware. The German CERT (CERT-Bund) has issued ...
-
 Cybersecurity News
CVE-2024-11667: Critical Vulnerability in Zyxel Firewalls Actively Exploited
CERT Germany (CERT-Bund) and Zyxel have warned of actively exploiting a critical vulnerability in Zyxel firewalls. This vulnerability tracked as CVE-2024-11667, is being leveraged to deploy Helldown r ...
-
Cybersecurity News
Zero-Day in Active Directory Certificate Services: Researcher Exposes CVE-2024-49019 with PoC
Security researchers from TrustedSec have uncovered a critical zero-day vulnerability, CVE-2024-49019, affecting Active Directory Certificate Services (AD CS). This flaw exploits a feature of version ...
-
Cybersecurity News
Evasive Malware Campaign Leverages CleverSoar Installer & Nidhogg Rootkit
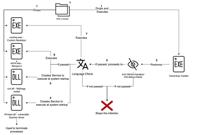
CleverSoar Attack Flow | Image: Rapid7Rapid7 Labs has uncovered a sophisticated malware campaign employing the newly identified CleverSoar installer, a highly evasive threat targeting Chinese and Viet ...

-
Cybersecurity News
Beyond FUD Links: Rockstar PaaS Kit Exploits Trusted Platforms for Phishing
The Rockstar Phishing-as-a-Service (PaaS) kit has caught the attention of cybersecurity experts for its advanced and devious tactics to bypass email defenses. In a report from Trustwave SpiderLabs, Ro ...
-
Cybersecurity News
Contiki-NG IoT OS Patches Critical Vulnerabilities
Researchers have identified and addressed three critical vulnerabilities in Contiki-NG, a popular open-source operating system for Internet of Things (IoT) devices. These vulnerabilities could allow a ...