


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 seclists.org
SCHUTZWERK-SA-2024-004: Buffer overread in U-Boot DHCP
Full Disclosure mailing list archives SCHUTZWERK-SA-2024-004: Buffer overread in U-Boot DHCP From: David Brown via Fulldisclosure <fulldisclosure () seclists org> Date: Fri, 23 Aug 2024 13:46:12 +0200 ...
-
 TheCyberThrone
Velvet Ant APT exploits Cisco bug CVE-2024-20399
Security researchers discovered that the China-linked APT group Velvet Ant has exploited the recently disclosed zero-day CVE-2024-20399 in Cisco switches to take over the network devices.Last month, C ...
-
 The Hacker News
CISA Urges Federal Agencies to Patch Versa Director Vulnerability by September
Vulnerability / Government Security The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has placed a security flaw impacting Versa Director to its Known Exploited Vulnerabilities (KEV) ca ...
-
TheCyberThrone
SolarWinds fixes CVE-2024-28987 in WHD Product
SolarWinds has released an update to a new security flaw in its Web Help Desk (WHD) software that could allow remote unauthenticated attackers to gain unauthorized access to vulnerable instances.The v ...

-
TheCyberThrone
Sonicwall fixes CVE-2024-40766 in SonicOS
SonicWall has released patch for a critical vulnerability affecting their SonicOS and could allow unauthorized access to SonicWall firewalls, potentially leading to a complete system compromise.The v ...
-
 Cybersecurity News
CVE-2024-39717: Versa Networks Director GUI Flaw Under Active Attack, CISA Issues Urgent Patching Directive
In a recent cybersecurity alert, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) has highlighted the active exploitation of a severe vulnerability identified as CVE-2024-39717. This f ...
-
Cybersecurity News
ALBeast Vulnerability Exposes Thousands of AWS Applications to Critical AuthN/AuthZ Bypass
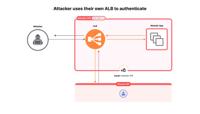
ALBeast attack demonstration | Image: MiggoA new configuration-based vulnerability, dubbed ALBeast, has been uncovered by Miggo Research, affecting a staggering number of applications relying on AWS A ...
-
Cybersecurity News
New PostgreSQL Threat: PG_MEM Malware Strikes Databases
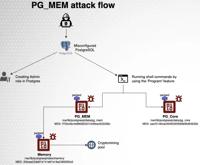
Attack flow of PG_MEM | Image: Aqua NautilusA new and insidious threat has emerged, targeting the widely used PostgreSQL database management system. Aqua Nautilus researchers have identified a novel m ...

-
 Dark Reading
Patch Now: Second SolarWinds Critical Bug in Web Help Desk
Source: SOPA Images LimitedFor the second week in a row, SolarWinds has released a patch for a critical vulnerability in its IT help and ticketing software, Web Help Desk (WHD).According to its latest ...
-
 BleepingComputer
Microsoft shares temp fix for Linux boot issues on dual-boot systems
Microsoft has provided a workaround to temporarily fix a known issue that is blocking Linux from booting on dual-boot systems with Secure Boot enabled. The company says this temporary fix can help Li ...