


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 Cybersecurity News
Log4j Exploited Again: New Campaign Targets Vulnerable Systems with Crypto-Mining and Backdoors
Despite its discovery over two years ago, the Log4j vulnerability, known as Log4Shell (CVE-2021-44228), continues to pose a significant threat to global cybersecurity. A recent report from Datadog Sec ...
-
Cybersecurity News
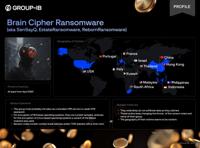
Beyond the Ransom: Inside the Mind of Brain Cipher Ransomware Group
Indonesian government agencies have fallen victim to a large-scale cyberattack orchestrated by the Brain Cipher ransomware group. On June 20, 2024, hackers dealt a severe blow to the country’s critica ...
-
Cybersecurity News
Urgent Chrome Update: Active Zero-Day Exploit Detected (CVE-2024-7971)
Google has released an urgent Chrome update (version 128.0.6613.84/85) in response to an actively exploited zero-day vulnerability (CVE-2024-7971). This vulnerability, categorized as a type confusion ...
-
Cybersecurity News
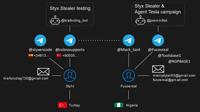
Styx Stealer: The Evolved Threat to Your Crypto and Data
Recently, Check Point Research (CPR) discovered a new malware variant, Styx Stealer. Derived from the notorious Phemedrone Stealer, Styx was being sold via subscription with advanced capabilities such ...
-
 TheCyberThrone
Spring Security fixes CVE-2024-38810
A high-severity flaw has been discovered in Spring Security, potentially allowing unauthorized access to sensitive data within affected applications.Spring Security’s powerful method security features ...
-
 The Register
You probably want to patch this critical GitHub Enterprise Server bug now
A critical bug in GitHub Enterprise Server could allow an attacker to gain unauthorized access to a user account with administrator privileges and then wreak havoc on an organization's code repositori ...
-
 BleepingComputer
Google fixes ninth Chrome zero-day exploited in attacks this year
Today, Google released a new Chrome emergency security update to patch a zero-day vulnerability tagged as exploited in attacks. "Google is aware that an exploit for CVE-2024-7971 exists in the wild, ...
-
BleepingComputer
Google fixes ninth Chrome zero-day tagged as exploited this year
Today, Google released a new Chrome emergency security update to patch a zero-day vulnerability tagged as exploited in attacks. "Google is aware that an exploit for CVE-2024-7971 exists in the wild, ...
-
The Register
Microsoft's Patch Tuesday borks dual-boot Linux-Windows PCs
Microsoft says it's investigating issues with a patch intended to plug a two-year-old flaw in the GRUB open source boot loader that is crashing some dual-boot computers running both Windows and Linux. ...
-
 Dark Reading
'Styx Stealer' Blows Its Own Cover With Sloppy OpSec Mistake
Source: BLKstudio via ShutterstockSecurity researchers were able to gather valuable information on the creator of a sophisticated new malware tool called Styx Stealer because of a basic operational se ...