


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 Cybersecurity News
New Zero-Day Emerges After Microsoft Patch Tuesday: CVE-2024-43461 Targets Windows MSHTML
IE and a promote window dialog appear when the victim double-clicks on the .url file | Image: Check PointIn an unexpected turn of events, Microsoft has revised its September 2024 Patch Tuesday securit ...

-
Cybersecurity News
CVE-2024-38816: Spring Framework Path Traversal Vulnerability Threatens Millions
A serious security vulnerability, identified as CVE-2024-38816 (CVSS 7.5), has been discovered in the popular Spring Framework, potentially affecting millions of Java applications worldwide. This path ...

-
Cybersecurity News
PoC Exploit Released for Ivanti EPM Flaw CVE-2024-29847 (CVSS 10)
Image: Horizon3.aiSecurity researcher James Horseman from Horizon3.ai has disclosed the technical details and a proof-of-concept (PoC) exploit code for a critical vulnerability (CVE-2024-29847) in Iva ...
-
Cybersecurity News
Ajina.Banker: Unmasking the Android Malware Targeting Central Asian Banks
Screenshot of the sample found on the VirusTotal platformCybersecurity analysts at Group-IB have uncovered a sophisticated malware campaign targeting bank customers in Central Asia. Dubbed “Ajina.Bank ...
-
Cybersecurity News
Don’t Fall for the Bait: Poseidon Stealer Masquerades as Sopha AI
Dialog box prompting the user to enter the password | Image: TRUIn a new wave of cyberattacks, macOS users are being targeted by the Poseidon Stealer malware, disguised as an installer for the highly ...

-
Cybersecurity News
Critical Flaw in NixOS Package Manager: CVE-2024-45593 Allows Arbitrary File Write with Root Permissions
A high-severity security flaw has been discovered in Nix, the popular package manager for Linux and Unix-based systems. Identified as CVE-2024-45593, this vulnerability poses a significant threat, all ...
-
Cybersecurity News
BadIIS Malware : 35+ IIS Servers Compromised in DragonRank Campaign
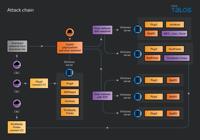
A recent report from Cisco Talos has exposed a new threat actor named DragonRank, a Chinese-speaking group specializing in SEO manipulation and cyberattacks. This group operates by exploiting vulnerab ...
-
 BleepingComputer
Windows vulnerability abused braille “spaces” in zero-day attacks
A recently fixed "Windows MSHTML spoofing vulnerability" tracked under CVE-2024-43461 is now marked as previously exploited after it was used in attacks by the Void Banshee APT hacking group. When fir ...

-
 TheCyberThrone
Docker Desktop bugs CVE-2024-8695 and CVE-2024-8696 fixed
Docker Desktop has been found to have two critical security vulnerabilities that could enable remote code execution (RCE) attacks.The vulnerabilities, tracked as CVE-2024-8695 with a CVSSv4 score of 9 ...

-
TheCyberThrone
Citrix Workspace vulnerabilities fixed
Cloud Software Group has disclosed two vulnerabilities affecting Citrix Workspace app for Windows that could allow a malicious actor with low-level access to escalate their privileges to the highest l ...