


CVEFeed Newsroom – Latest Cybersecurity Updates
The "Cyber Newsroom Feed" module is a live feed of the latest cyber news enriched with CVE and vulnerability data. The feed is updated every 10 minutes and includes the latest news from the cyber security industry. The feed is designed to provide users with a comprehensive overview of the latest cyber security news and trends.
-
 Cybersecurity News
166k+ Projects at Risk: AutoGPT’s Critical Vulnerability Explained – CVE-2024-6091 (CVSS 9.8)
A significant security vulnerability has been discovered in AutoGPT, a powerful AI tool designed to automate tasks through intelligent agents. With over 166k stars on GitHub, AutoGPT has gained popula ...
-
Cybersecurity News
Faraday: Open Source Vulnerability Management Platform
In today’s complex cybersecurity landscape, security teams face the dual challenge of uncovering new vulnerabilities and efficiently managing remediation efforts. Faraday emerges as a powerful solutio ...
-
Cybersecurity News
CISA Flags Two Actively Exploited Vulnerabilities: Critical Threats to Windows and WhatsUp Gold
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued a warning, adding two actively exploited security flaws to its Known Exploited Vulnerabilities (KEV) catalog, urging immedia ...
-
Cybersecurity News
Critical Flaws Found in VICIdial Contact Center Suite: CVE-2024-8503 and CVE-2024-8504, PoC Published
In a concerning development for call centers using VICIdial, a popular open-source contact center solution, two high-severity security vulnerabilities have been discovered that could lead to severe da ...
-
Cybersecurity News
Exploit Kits, Cryptominers, Proxyjackers: The New Face of Selenium Grid Abuse
Researchers at Cado Security Labs have uncovered two malicious campaigns that exploit misconfigured instances of Selenium Grid. Once a trusted tool for browser automation and testing, Selenium Grid ha ...
-
 The Register
Microsoft confirms IE bug squashed in Patch Tuesday was exploited zero-day
Analysis Microsoft, in a low-key update to its September Patch Tuesday disclosures, has confirmed a just-fixed Internet Explorer vulnerability was exploited as a zero-day before it could be patched. R ...
-
Cybersecurity News
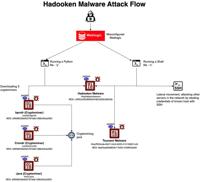
Hadooken Malware: A New Threat to WebLogic Servers
The entire attack flow | Image: Aqua NautilusCybersecurity researchers at Aqua Nautilus have discovered a new Linux malware strain, dubbed “Hadooken,” that is specifically targeting Oracle WebLogic se ...
-
 Ars Technica
Secure Boot-neutering PKfail debacle is more prevalent than anyone knew
THIS IS NOT A TEST — Keys were marked "DO NOT TRUST." More devices than previously known used them anyway. Getty Images A supply chain failure that compromises Secure Boot protections on computing ...
-
 Dark Reading
'Void Banshee' Exploits Second Microsoft Zero-Day
Source: Anucha Cheechang via ShutterstockMicrosoft has recategorized a bug that the company fixed in this month's Patch Tuesday update as a zero-day vulnerability, which the "Void Banshee" advanced pe ...

-
Dark Reading
Ivanti Cloud Bug Goes Under Exploit After Alarms Are Raised
Source: NicoElNino via Alamy Stock PhotoJust days after Ivanti released an advisory regarding a high-severity vulnerability in its Cloud Service Appliance (CSA), the company is alerting customers that ...